 Hack the Route Start free Open app
The idea
webServer, fileServer and coreRouter, a Router, push their log lines to logServer, one collector, a syslog server, which sorts them by host and severity. A laptop sits in the office.
Steps
-
A log line travels to the collector
Logs kept on each device are scattered, and lost with the device, so devices send them to one place. Like an SNMP trap, a log line is the device speaking first. Log one line on webServer while logServer records UDP Port 514.
webServer:~# logger 'disk almost full'
logServer:~# cat /var/log/remote/webServer.log
-
Facility and severity: the PRI number
Each line says how serious it is, so a collector can sort and filter. Each message starts with a number, the PRI: facility × 8 + severity. Severity runs from 0 (
emerg) to 7 (debug); lower is worse.auth(logins) is facility 4,critseverity 2.webServer:~# logger -p auth.crit 'Failed password for root' logServer:~# tail -1 /var/log/remote/webServer.log
Pro
4 more steps in the app
- One file per host
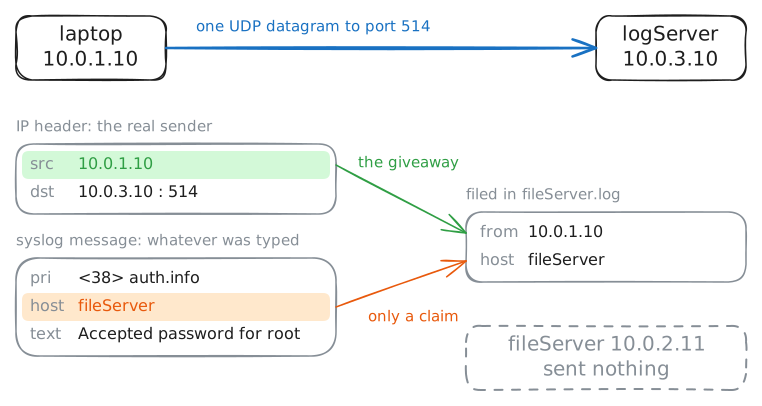
- The host name is only a claim
- Filtering by severity
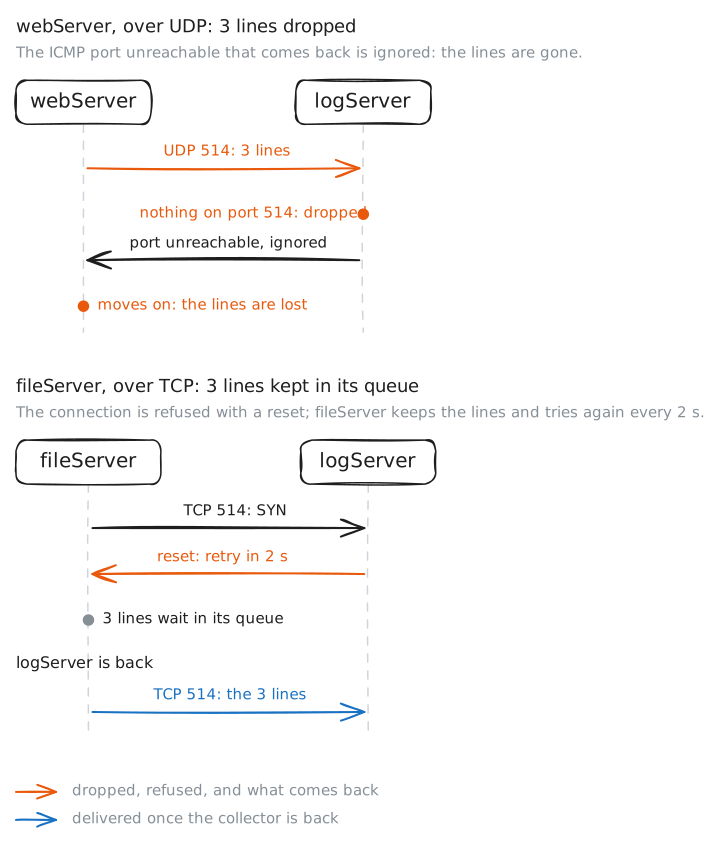
- When the collector is down