 Hack the Route Start free Open app
The idea
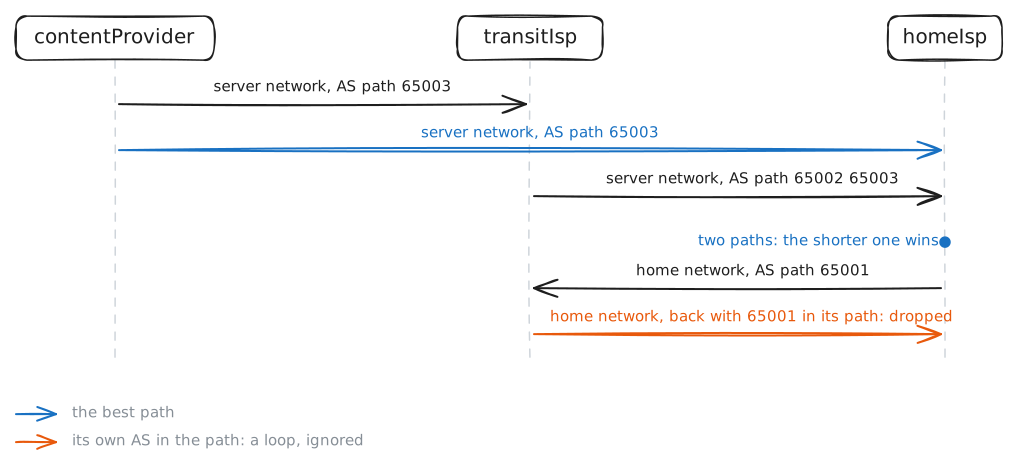
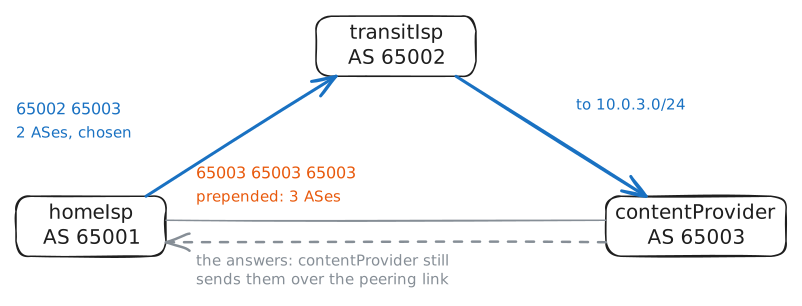
With BGP, homeIsp, transitIsp and contentProvider, networks run by different organisations, tell each other which addresses they reach and through whom. A laptop at homeIsp reaches contentProvider's web server by the shortest list of networks.
Steps
-
Sessions over TCP
homeIsp, a home ISP, swaps routes with two other organisations: transitIsp and contentProvider. In vtysh, FRR's shell, list its BGP sessions, then the connections under them.
homeIsp:~# vtysh
homeIsp:~# ss -tn state established '( sport = :179 or dport = :179 )'
-
Who can reach what: the AS path
Read homeIsp's BGP table: every network it heard of, and through whom. Then read transitIsp's, in the middle. This table is how BGP chooses a way and avoids loops, so reading it is the core skill.
homeIsp:~# vtysh
transitIsp:~# vtysh
Pro
3 more steps in the app
- The shortest AS path wins
- Steering traffic from the other side: prepending
- A link breaks: the hold timer