 Hack the Route Start free Open app
The idea
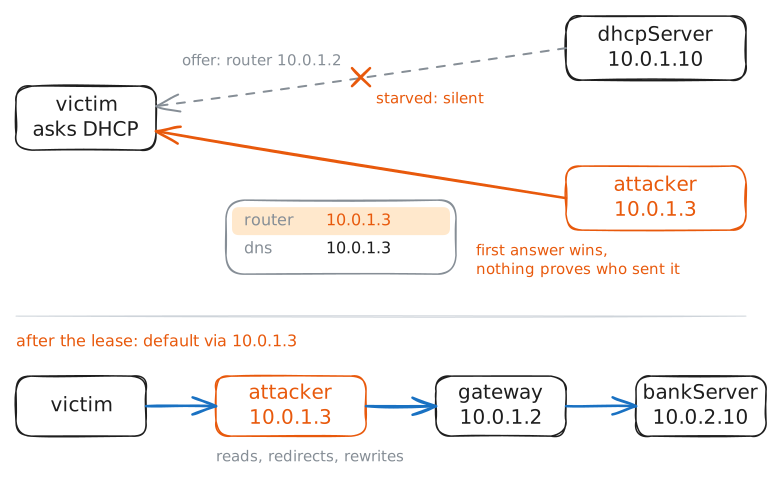
A joining device takes the first DHCP offer it hears, and the offer names its gateway and DNS — with nothing to prove who sent it. A rogue DHCP server on the same wire answers with itself, so the victim sends every packet through the attacker, which forwards them on while it reads or redirects whatever it likes.
Steps
-
A network that trusts any offer
The victim already holds a lease from the real server. Its default route points at the real gateway
10.0.1.2, and it reaches the bank through it. Note that gateway — the attack's whole aim is to change it.victim:~# ip route show default victim:~# curl -s --max-time 5 http://10.0.2.10/
-
The rogue server appears
The attacker stands up its own DHCP server on the same wire, handing out itself (
10.0.1.3) as gateway and DNS. Now two servers answer. Send a discover from the victim and list who offers — the rogue names itself.victim:~# nmap --script broadcast-dhcp-discover -e eth0
Pro
3 more steps in the app
- Winning the race by starvation
- In the middle
- Defence: trust only the right server