 Hack the Route Start learning Open app
Cloud security
Infrastructure-as-code security
Cloud estates are built from declarative code; the misconfiguration ships from a line in that code, so the cheapest place to catch it is the review.
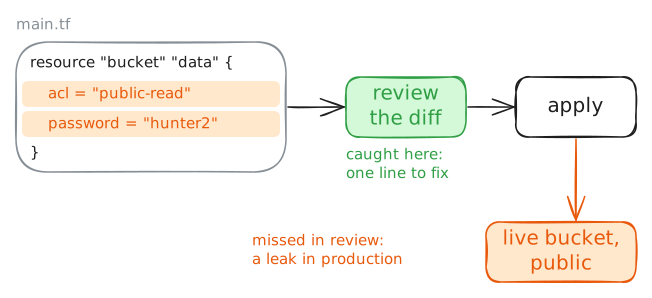
Infrastructure as code (IaC) is declaring cloud resources in files, such as Terraform or CloudFormation, and
applying them to create the real ones. A misconfiguration is a line in a file first: a bucket with a public ACL, a
plaintext password. Catching it in review, before apply, is called shift-left. Fix it in the same file:
private ACL, secret in a secret store. That prevents [[cloud-storage-exposure|public cloud storage]].