 Hack the Route Start learning Open app
Binary exploitation
Memory disclosure
Making a program hand back memory it never meant to reveal — classically through a format string built from untrusted input.
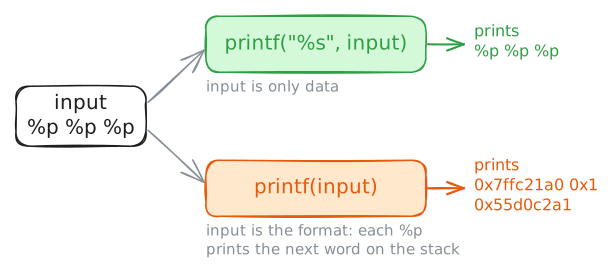
A memory disclosure makes a program print memory it never meant to reveal. The classic is the format-string
bug: printf(user_input) instead of printf("%s", user_input). printf then obeys the input: each %p prints a
stack word, %s prints the string a stack word points to. That leaks secrets and addresses, and one leaked address
defeats [[stack-overflow|ASLR]]. The fix: untrusted input is never the format; -Wformat-security warns about it.