 Hack the Route Start learning Open app
Network attacks
VLAN hopping
Escaping the VLAN your port is assigned to and reaching another one — classically by wrapping a frame in two 802.1Q tags so the first switch strips the outer and forwards the inner into a VLAN you were never meant to touch.
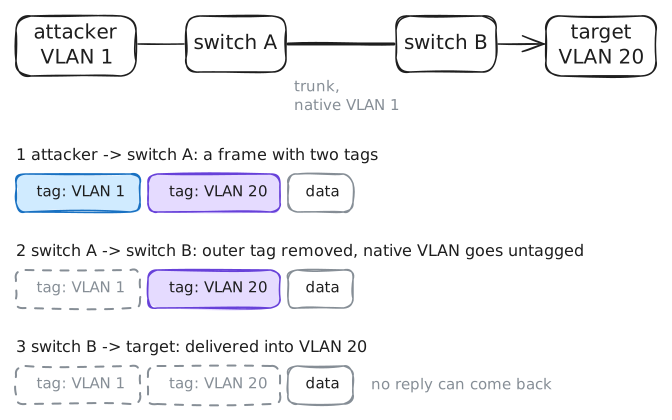
VLAN hopping is sending frames into a [[vlan|VLAN]] your port is not in. In double tagging, an attacker on a [[trunk|trunk]]'s native VLAN sends a frame with two 802.1Q tags. The first switch removes the outer tag, because the native VLAN crosses the trunk untagged; the second switch reads the inner tag and delivers it into the target VLAN. It is one-way: no reply returns. Fix: an unused native VLAN.