 Hack the Route Start free Open app
The idea
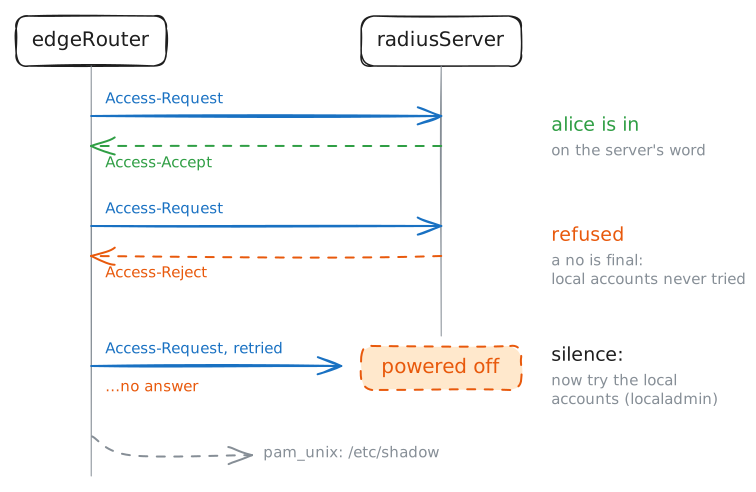
AAA puts every Router's logins on one server. edgeRouter asks radiusServer about each login from the laptop over RADIUS: who you are, what you may do, and a log of each session. Its own break-glass account works only while the server is silent.
Steps
-
A login the router does not decide
edgeRouter holds no password for alice, so one change on the server reaches every router. alice logs in over SSH; the router sends her name and password to radiusServer in an Access-Request and obeys the answer.
laptop:~# sshpass -p correct-horse ssh alice@10.0.1.2 'show privilege'
-
A wrong password: Access-Reject
bob types the wrong password. Both sides log it, because refused logins are the first thing to read after a break-in. Log in as bob with
letmein, then read the server's log and the router's.laptop:~# sshpass -p letmein ssh bob@10.0.1.2 'show privilege' radiusServer:~# grep 'Login incorrect' /var/log/radius.log edgeRouter:~# tail -1 /var/log/aaa.log
Pro
4 more steps in the app
- Authorization: what each one may do
- Accounting: who was on, and for how long
- The server is down: the local account
- Back up: the local account is not a back door