 Hack the Route Start free Open app
The idea
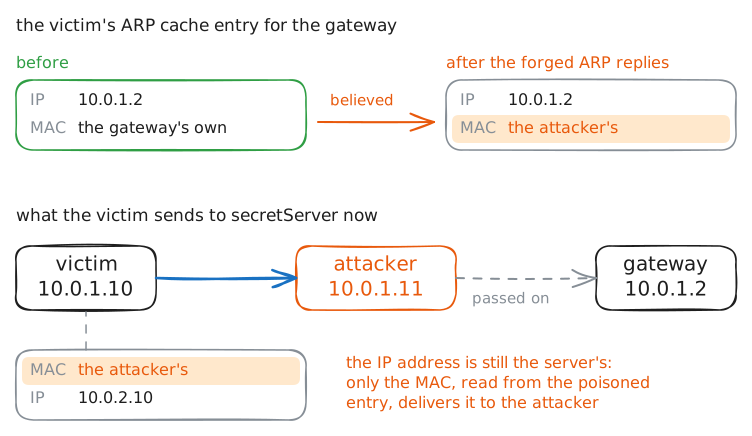
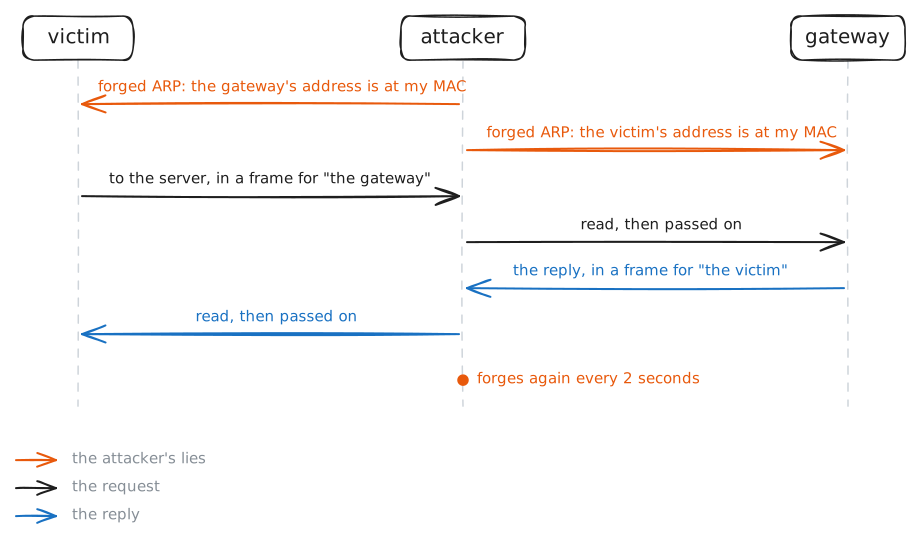
On a shared network, ARP spoofing lets anyone claim the gateway's address and sit in the middle — a man in the middle attack — and only TLS still protects what crosses it.
Steps
-
A quiet network
See the victim's normal view first: it holds the gateway's real MAC and reads its bank account straight through it. Note that MAC — the attack will swap it.
victim:~# ip neigh show 10.0.1.2
victim:~# curl -s http://bank.lab/account
-
Poison the caches
Turn the attack on. The attacker floods forged ARP, claiming the gateway's address for its own MAC. List the victim's neighbours and watch two addresses end up at one MAC.
victim:~# ip neigh show
Pro
4 more steps in the app
- Still working, now watched
- HTTPS goes dark
- To tamper, break TLS
- Pull the attacker out