 Hack the Route Start free Open app
The idea
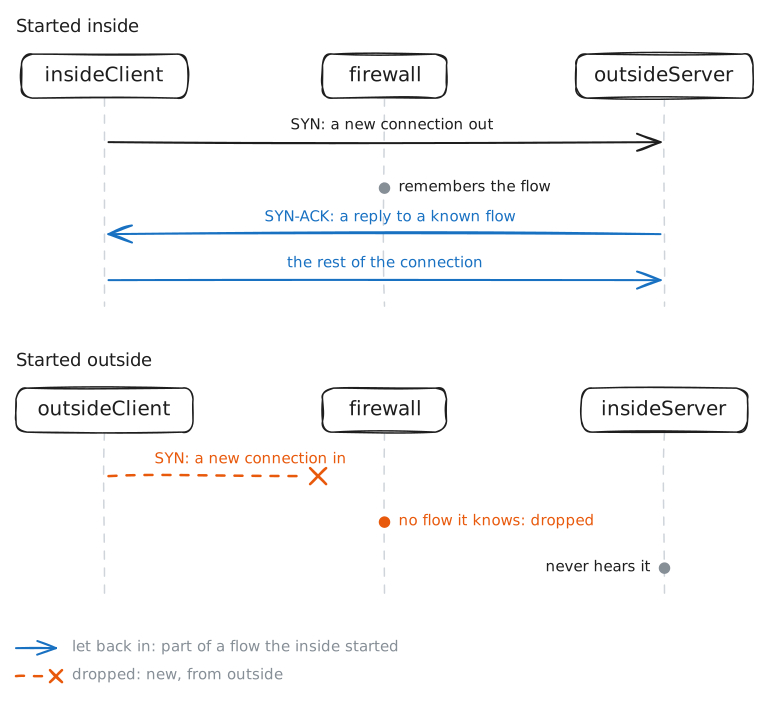
A stateful Firewall remembers the connections it let out, so their replies come home and nothing new comes in. You build one on firewall, between insideClient and insideServer on one side and outsideClient and outsideServer on the other.
Steps
-
The inside reaches out
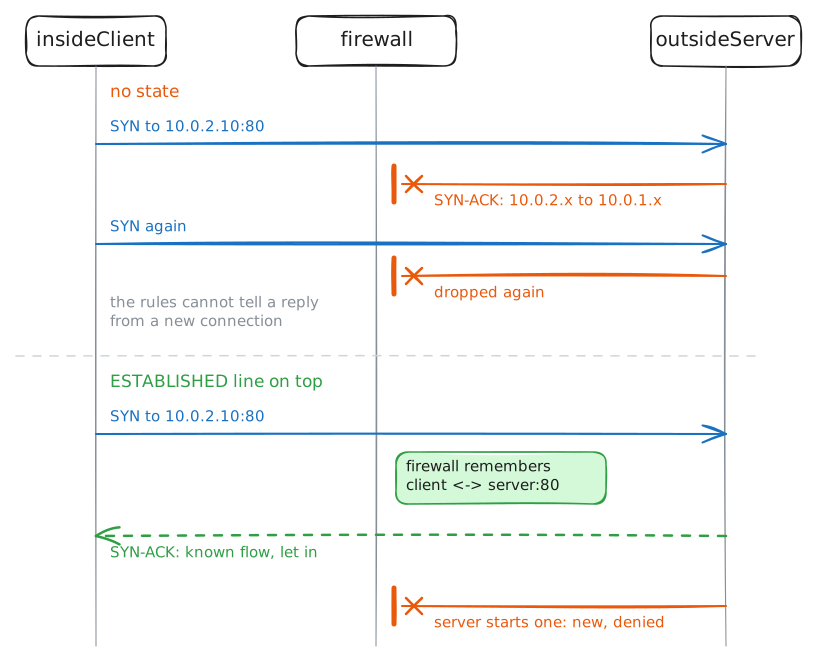
Build a stateful firewall from nothing, starting with rules that judge each packet alone, to see why that is not enough. First the plain part: accept whatever the inside sends, and drop everything else with the
FORWARDpolicy.firewall:~# iptables -A FORWARD -i insideNetwork -j ACCEPT firewall:~# iptables -P FORWARD DROP insideClient:~# curl -sS -m 4 http://outsideServer.lab/
-
Replies need state
A reply is a packet from the outside too, so the firewall must remember what it let out to tell the two apart. Above step 1's rules, put a line that accepts packets of a connection the firewall already let through: established, by its connection tracking.
firewall:~# iptables -I FORWARD 1 -m conntrack --ctstate ESTABLISHED,RELATED -j ACCEPT
insideClient:~# curl -sS -m 4 http://outsideServer.lab/
firewall:~# conntrack -L -p tcp --dport 80
Pro
2 more steps in the app
- The outside is shut out
- It is the direction, not the host