 Hack the Route Start free Open app
The idea
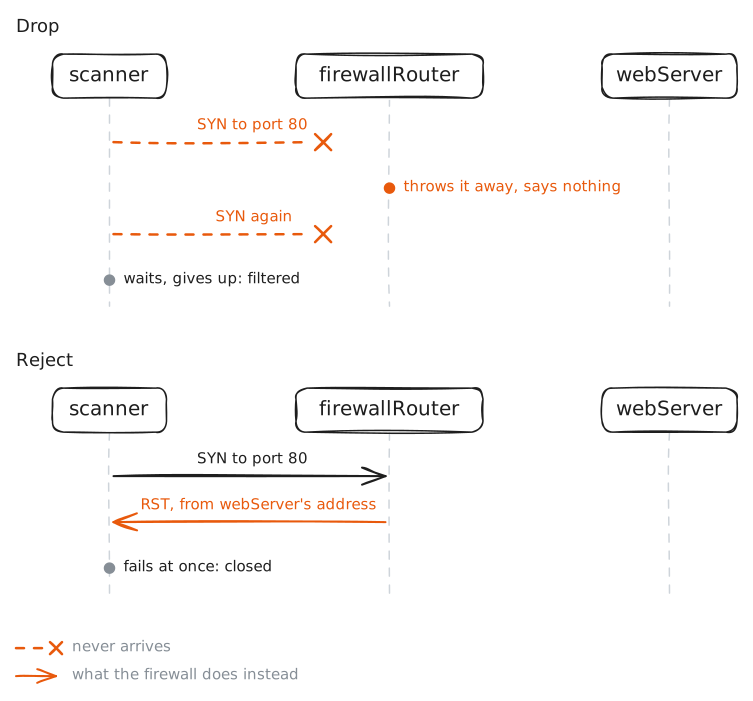
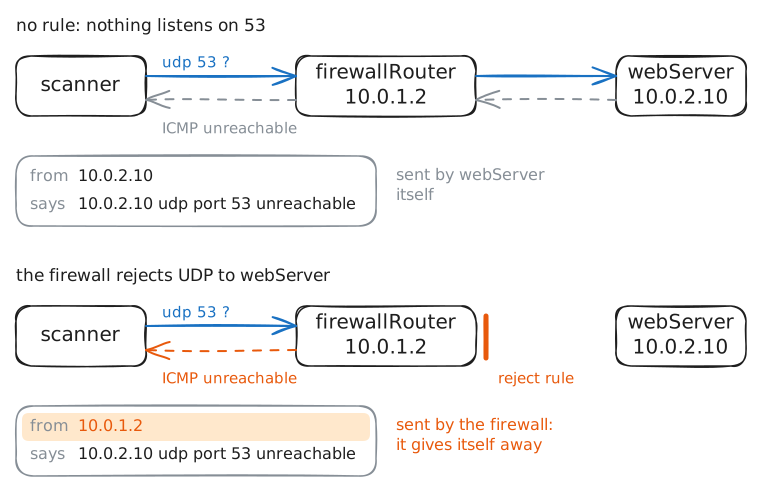
A Firewall that blocks can drop the packet and stay silent, or reject it and say no; drop vs reject, a scanner learns something from either. Here the scanner probes webServer through firewallRouter, whose rules you write.
Steps
-
Scan the server with nothing in the way
An attacker maps a network by scanning it, so first see what a scan reports when nothing is in the way.
nmapsends a SYN to each Port and names the port by what comes back. The web server listens on 80 and 443; nothing listens on 22.scanner:~# nmap -Pn -p 22,80,443 webServer.lab
-
Drop port 80
Silence is the first way to block: the sender gets nothing back to learn from. Make firewallRouter throw away every packet to port 80, without a word. iptables'
FORWARDchain holds the rules for packets it passes on.firewallRouter:~# iptables -A FORWARD -p tcp --dport 80 -j DROP scanner:~# curl -sS -m 5 http://webServer.lab/ scanner:~# nmap -Pn -p 80 webServer.lab
Pro
3 more steps in the app
- Reject port 80 instead
- UDP gives the firewall away
- Drop everything to the server