 Hack the Route Start free Open app
The idea
A reverse proxy answers for a server; as a web application Firewall it reads each request and refuses the attacks a packet filter cannot see. Here customers reach shopApp only through waf, and edgeRouter lets nothing else in.
Steps
-
A reverse proxy in front of the shop
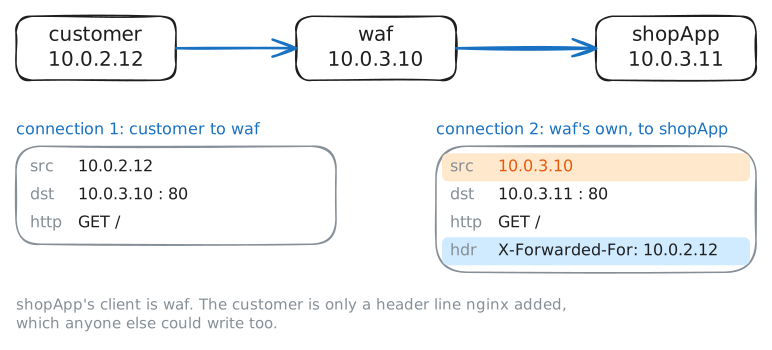
Putting one machine in front of the shop gives a single place to read and refuse requests before the shop sees them. Customers reach the shop only through
waf, a reverse proxy: it takes each request and passes it toshopAppover a connection of its own.customer:~# curl -s http://waf.lab/ shopApp:~# tail -n 2 /var/log/httpd.log
-
The WAF says no
A packet filter sees only addresses and ports, so an attack inside an ordinary request passes it. A web application firewall (WAF) reads each request before passing it on. Its rules refuse
/adminpaths, scanners' user agents and SQL injection in the arguments.customer:~# curl -sI http://waf.lab/admin/ customer:~# curl -sI "http://waf.lab/search?q=1+or+1=1" customer:~# curl -s "http://waf.lab/search?q=shoes" waf:~# tail -n 2 /var/log/nginx/waf.log
Pro
3 more steps in the app
- A rule too broad
- Too many requests
- Packets, connections, requests