 Hack the Route Start learning Open app
Exploitation and privilege escalation
Exploit frameworks and C2
The tooling a tester layers on a foothold to manage access: a listener on a team server, an implant that calls home, and a session to task — plus the beaconing it leaves for defenders to catch.
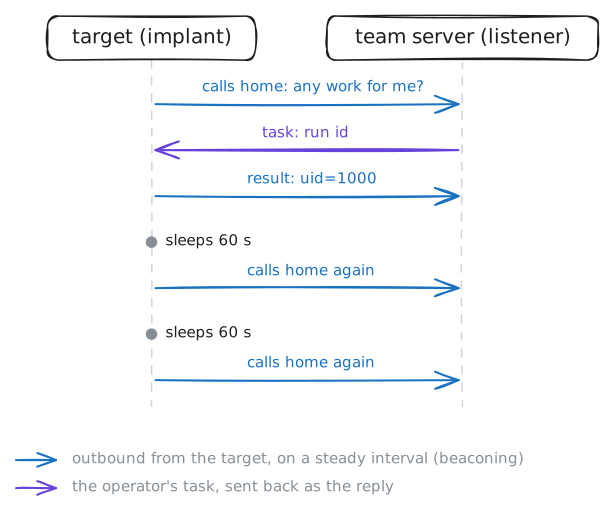
An exploit framework, or C2 (command and control), such as Metasploit or Sliver, turns one fragile shell into a managed session. Three parts: a listener on the team server, an implant delivered to the target, and the session opened when the implant calls home. The call is outbound, so inbound firewall rules miss it. It repeats on an interval; this beaconing rhythm shows in flow logs even when encrypted.