 Hack the Route Start learning Open app
Exploitation and privilege escalation
Privilege escalation
Turning a limited login on a host into full control, by abusing one thing the system was left doing wrong.
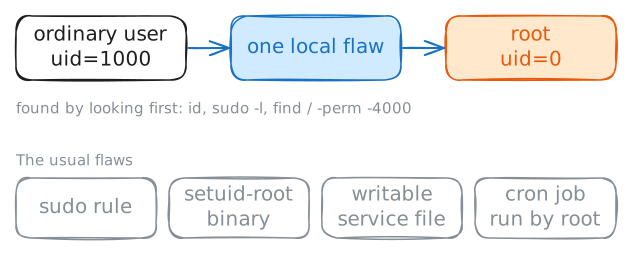
Privilege escalation is turning a limited login on a host into root (uid=0). It abuses one local flaw: a
sudo rule that runs a program as root, a [[setuid]] binary owned by root, a writable service file, or a root
cron job. Finding the flaw comes first: id, sudo -l, find / -perm -4000. The defence is least privilege: never
grant a command that can launch other commands.
Read next
- Setuid and setgid A permission bit that makes a program run as its owner, not as whoever started it — safe on a few tools, dangerous on one that runs other commands.
- GTFObins A catalogue of ordinary Unix binaries that can be bent into reading files, writing files or spawning a shell — the key to abusing a sudo rule or a setuid bit.
- SSH Encrypted remote login and commands, on TCP port 22, with passwords or keys.
- Password strength and rate limiting Why guessable passwords fall to repeated tries, and the defences that stop them.
- Exploit frameworks and C2 The tooling a tester layers on a foothold to manage access: a listener on a team server, an implant that calls home, and a session to task — plus the beaconing it leaves for defenders to catch.
- Getting a foothold Turning reconnaissance of a target into the first shell on it, by picking the one opening worth attacking and using the move it calls for.
- Default credentials The username and password a device or appliance ships with — a confirmed way in whenever nobody changes it before the box goes live.
- Stack buffer overflow Writing past a fixed stack buffer until the write reaches the function's saved return address, then choosing where the function returns to.