 Hack the Route Start learning Open app
Active reconnaissance
Firewalking
Using a port the firewall allows, plus TTL-limited probes, to map the routers and hosts hidden behind it.
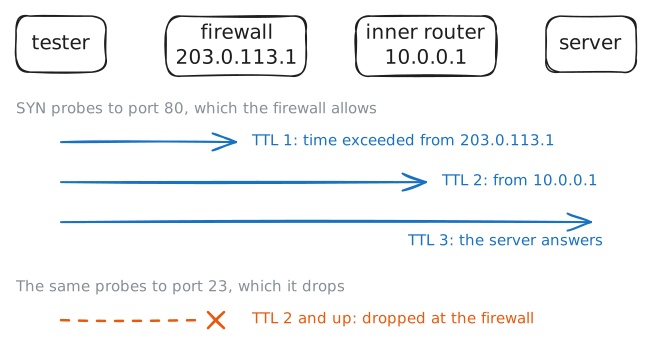
Firewalking maps the routers behind a firewall with [[ttl|TTL]]-limited probes sent to a port the firewall
allows. As in traceroute, the router where a probe's TTL reaches zero answers with an ICMP time-exceeded that
names it; an allowed probe passes the firewall, so routers inside answer too. hping3 --traceroute -S -p 80 does it
with TCP SYNs. The defence: block outgoing time-exceeded errors at the edge.
Read next
- Packet crafting Building one packet by hand — choosing every flag and field — to probe a target a single reply at a time.
- TTL A counter in every IP packet, lowered by each router; at zero the packet is dropped.
- Traceroute Lists the routers on the way to a destination, by sending packets with TTL 1, then 2, then 3.
- Stateful firewall A firewall that remembers connections, so it can allow replies while refusing new connections in.
- Drop or reject Two ways to refuse a packet: silence, or an explicit answer.