 Hack the Route Start learning Open app
Exploitation and privilege escalation
GTFObins
A catalogue of ordinary Unix binaries that can be bent into reading files, writing files or spawning a shell — the key to abusing a sudo rule or a setuid bit.
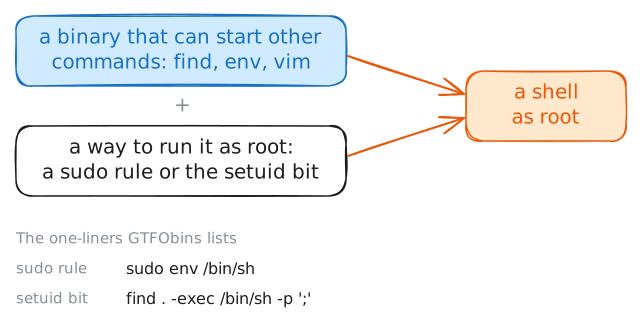
GTFObins (gtfobins.github.io) catalogues ordinary Unix binaries that can read a file, write a file or start a
shell. find runs commands with -exec, env runs any program, vim has a shell escape. Run as root, the shell
is root's: through a sudo rule (sudo env /bin/sh) or the [[setuid]] bit (find . -exec /bin/sh -p \;). That
is a [[privilege-escalation|privilege escalation]], so never grant such a binary elevated rights.
Read next
- Privilege escalation Turning a limited login on a host into full control, by abusing one thing the system was left doing wrong.
- Setuid and setgid A permission bit that makes a program run as its owner, not as whoever started it — safe on a few tools, dangerous on one that runs other commands.
- SSH Encrypted remote login and commands, on TCP port 22, with passwords or keys.