 Hack the Route Start learning Open app
The web
HTTP cookie
A short piece of text a server gives a client, which the client sends back on every later request.
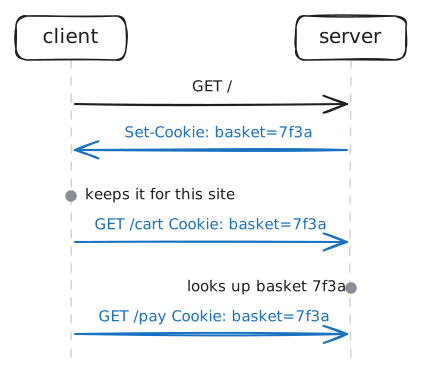
HTTP is stateless: nothing links one request to the next. A server sends Set-Cookie: basket=7f3a, the client
stores it, and every later request to that site carries Cookie: basket=7f3a. Usually the value is only a session
number, and the data stays on the server. Whoever holds the number is that visitor, so sign-in cookies are marked
Secure (HTTPS only) and HttpOnly (hidden from the page's scripts).
Read next
- HTTP The web's request and response protocol: plain text over TCP unless wrapped in TLS.
- TLS and certificates Encryption plus proof of identity: the server shows a certificate for the name, signed by a trusted authority.
- HTTP cache A stored copy of a reply, reused until it expires and then checked with the server.