 Hack the Route Start learning Open app
Monitoring
Packet capture
A copy of the packets crossing a network card, read live or saved to a file.
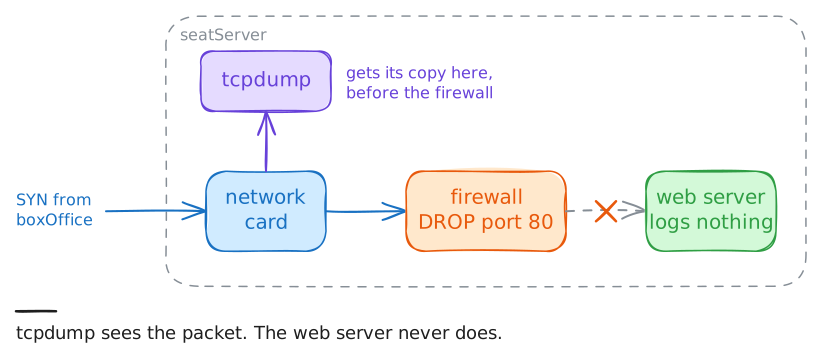
A packet capture copies what crosses a card, as tcpdump or Wireshark shows it, whatever the programs on the
machine believe. A capture filter decides what is saved and a display filter chooses what you see from a
saved file. On Linux the copy is taken at the card, before the firewall on the way in and after it on the way out,
so a packet in a capture has reached the card and may still never reach the program. A capture only sees what reaches
its own card: on a switched network that means capturing on an end machine, a mirror port or a tap.
Read next
- Port mirroring (SPAN) A switch copying every frame of some ports out of another port, where a sensor or capture box listens.
- Packet forensics Reconstructing an incident after the fact from a saved packet capture of the traffic.
- Three-way handshake SYN, SYN-ACK, ACK: how TCP opens a connection, each side agreeing on starting sequence numbers.
- Firewall Rules deciding, packet by packet, what may reach or cross a device.