 Hack the Route Start learning Open app
Passwords and hashes
Password spraying
Trying one likely password once against every account, so no account passes a lockout threshold and anyone who reused a weak shared secret is found.
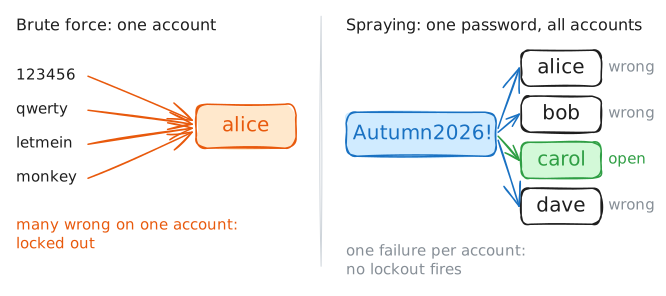
Password spraying tries one likely password once against every account. Brute force tries many passwords on one
account and trips its lockout; a spray fails once per account, so no lockout fires, and accounts using it open. It needs
a username list and one good guess, like an unchanged default. In hydra: -L the list, -p one password. A second
factor stops it; watch for one source touching many accounts.
Read next
- Online credential guessing Trying username/password pairs against a live service, as fast as it allows — and why it fails against hardened logins.
- Password strength and rate limiting Why guessable passwords fall to repeated tries, and the defences that stop them.
- Key-based authentication Logging in with a private key whose public half the server trusts, instead of a password — so password guessing cannot work.