 Hack the Route Start learning Open app
Security foundations
Rules of engagement
The signed document that says which systems a tester may touch, how, and when — the line between a penetration test and a crime.
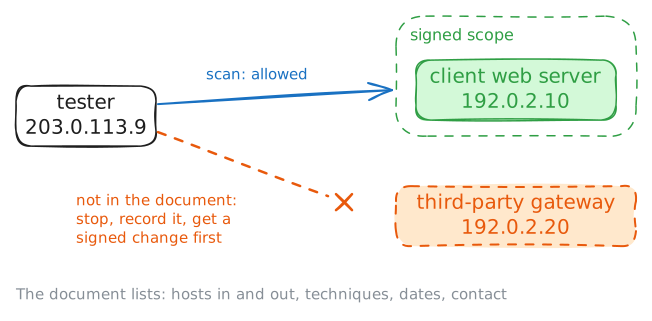
The rules of engagement are the signed agreement on which systems a penetration tester may touch, how and when. It lists hosts in scope by name and address, what is out of scope, the techniques allowed, the dates, the tester's source address and a contact. Anything found outside it is not touched: stop, document, get a signed change. The UK Computer Misuse Act and the US CFAA turn on authorisation.