 Hack the Route Start learning Open app
Cloud security
Serverless injection
A serverless function that folds untrusted input into a template or format string can be driven to reflect its own environment — where its role credentials live.
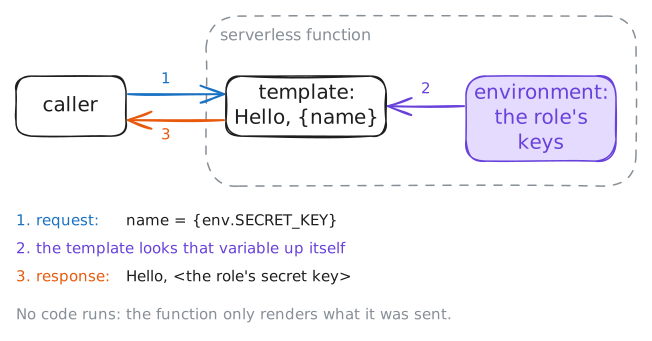
Serverless injection makes a serverless function print its own secrets. The platform passes the function its
role's credentials in environment variables. If caller input is folded into a template or format string that
can resolve variables ({env.KEY}), a crafted field makes the response include them. No code execution is needed.
Treat input as data, never as template, and scope the role ([[cloud-least-privilege]]). Compare
[[instance-metadata-ssrf|the metadata service]].
Read next
- Instance metadata & SSRF Every cloud instance reads its role's short-term keys from a link-local metadata service; an app with an SSRF can be made to read them for an attacker.
- Least privilege (cloud IAM) A cloud access key should grant only the exact actions and resources its job needs; a wildcard grant hands over far more.
- Command injection Running your own operating-system commands by sending input a web app pastes into a shell command line.