 Hack the Route Start learning Open app
Web access and file flaws
Unrestricted file upload
Letting a user upload any file with no check on its type, so attacker code can be stored on the server.
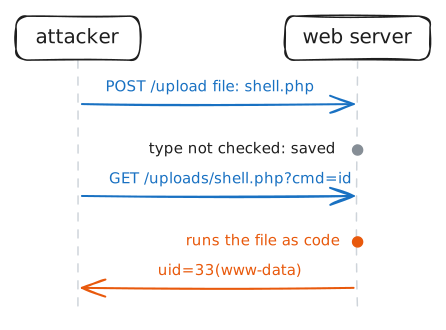
Unrestricted file upload is an upload form that saves any file without checking its type. An attacker uploads a web shell, a script that runs commands for whoever opens it. If the server executes that file type (.php, .jsp, .aspx), opening the stored file runs the attacker's code. The fix: an allow-list of file types, uploads stored outside any folder the server executes, and names the server chooses.
Read next
- Path traversal Reading files outside the intended folder by putting `../` in a filename the server joins onto a path.
- HTTP The web's request and response protocol: plain text over TCP unless wrapped in TLS.
- Command injection Running your own operating-system commands by sending input a web app pastes into a shell command line.