 Hack the Route Start learning Open app
Web access and file flaws
Path traversal
Reading files outside the intended folder by putting `../` in a filename the server joins onto a path.
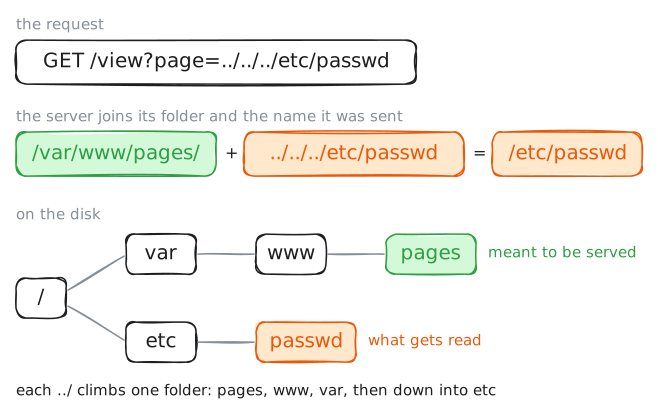
Path traversal is reading files outside the intended folder by putting ../ in a file name the server joins onto a path. If the server opens pages/<name> without checking the name, ../../../../etc/passwd climbs out of the folder and reads any file the server process can open: password files, keys, configuration. The fix: resolve the path and reject anything outside the folder, or serve only a fixed set of known names.
Read next
- Unrestricted file upload Letting a user upload any file with no check on its type, so attacker code can be stored on the server.
- HTTP The web's request and response protocol: plain text over TCP unless wrapped in TLS.
- Content discovery Finding the pages and files a web server holds but links to nowhere, by guessing common paths from a wordlist.