 Hack the Route Start learning Open app
Social engineering
Watering-hole attack
Compromising a legitimate site a target group already trusts and visits, so the payload reaches the targets through a site they came to on their own.
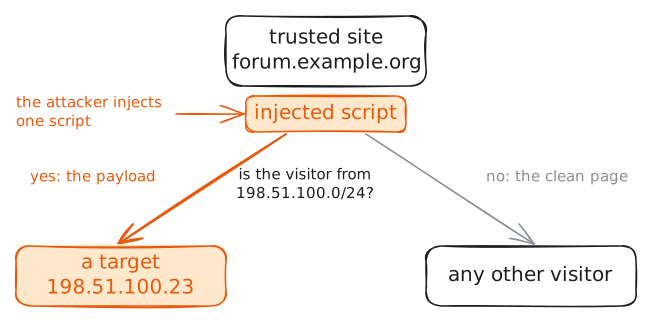
A watering-hole attack compromises a legitimate site the targets already visit, instead of luring them somewhere new. The attacker injects a script into the trusted site. It profiles each visitor (address range, cookie, user-agent) and delivers its [[beaconing|payload]] only to the intended victims; everyone else, the site's operators included, gets a clean page, so it is hard to catch. Defences on the site: patching, Subresource Integrity, a Content Security Policy.
Read next
- Phishing A message that impersonates someone a target trusts to make them act — click a link, hand over a login, open a file — before they think.
- Beaconing A compromised host repeatedly contacting an outside controller to fetch commands, on a regular rhythm.
- Drive-by download A page that pushes a file to a visitor's machine with little or no consent — the delivery step of an attack, separate from whatever the file then tries to do.
- Indicators of compromise (IOC) Concrete artifacts of an attack — an address, a file path, a hash — that you block and hunt for everywhere.
- Pretext The believable story a social-engineering attack wraps around its request so the target acts on it without checking.