 Hack the Route Start learning Open app
Exploitation and privilege escalation
Getting a foothold
Turning reconnaissance of a target into the first shell on it, by picking the one opening worth attacking and using the move it calls for.
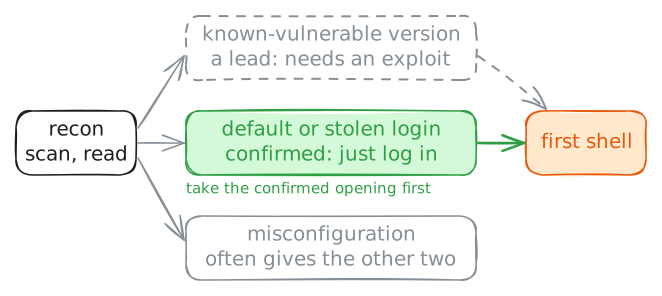
A foothold is the first session on a target, usually as an ordinary user, not root. Reconnaissance turns up three kinds of opening: a known-vulnerable version (only a lead until an exploit is confirmed), a [[default-credentials|default or stolen credential]] (a confirmed way in: just log in), and a misconfiguration, which often hands over one of the other two. Take the confirmed opening first; keep an unconfirmed exploit as a fallback.
Read next
- Default credentials The username and password a device or appliance ships with — a confirmed way in whenever nobody changes it before the box goes live.
- Privilege escalation Turning a limited login on a host into full control, by abusing one thing the system was left doing wrong.
- Port scanning Probing an address's ports to learn which services it exposes, and whether a firewall sits in the way.
- Banner grabbing Reading the greeting a service sends on connect, to learn the real software and version behind a port.