 Hack the Route Start learning Open app
Exploitation and privilege escalation
Default credentials
The username and password a device or appliance ships with — a confirmed way in whenever nobody changes it before the box goes live.
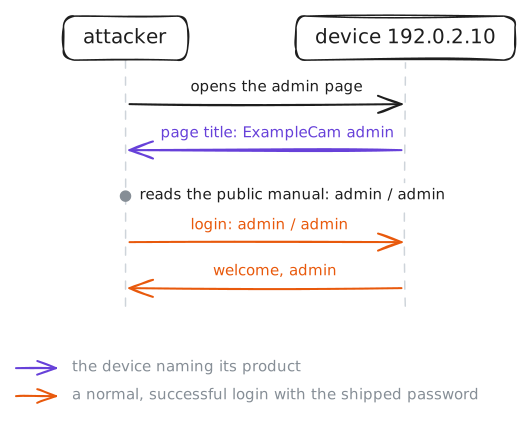
Default credentials are the username and password a device, database or admin panel ships with, such as
admin/admin, so an operator can log in on first boot. They are published, so anyone who learns the product (from a
banner or a page title) knows the login. Unchanged, they are a way in that needs no exploit, looks like a normal
successful login, and survives patching. Change every default before go-live.
Read next
- Getting a foothold Turning reconnaissance of a target into the first shell on it, by picking the one opening worth attacking and using the move it calls for.
- Privilege escalation Turning a limited login on a host into full control, by abusing one thing the system was left doing wrong.
- Password strength and rate limiting Why guessable passwords fall to repeated tries, and the defences that stop them.
- SSH Encrypted remote login and commands, on TCP port 22, with passwords or keys.
- Vulnerability classes Vulnerabilities sorted by kind, because the kind decides the fix: patch, change, reconfigure, validate, or rotate and remove.