 Hack the Route Start learning Open app
Web injection and scripting
Output encoding
Escaping untrusted data for the exact place it is written, so it is shown as text and never run as code.
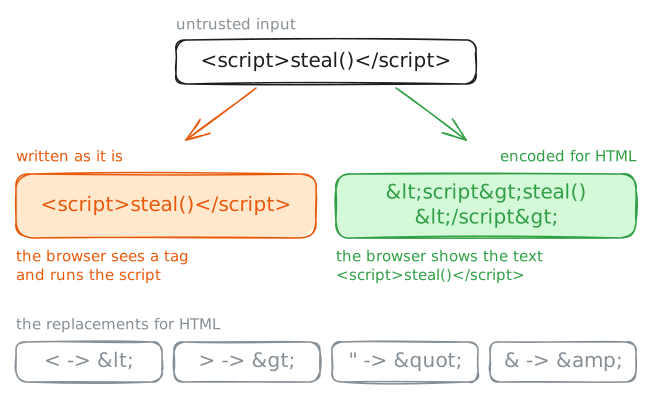
Output encoding is escaping untrusted data for the exact place it is written, so the browser shows it as text and never runs it. In HTML, < becomes < and a quote ". Each context (HTML body, attribute, URL, <script> block, CSS) has its own rules, so it is done at output, not input. It is the main defence against [[cross-site-scripting|XSS]]. Templates escape by default; bugs come from raw output.