 Hack the Route Start learning Open app
Web injection and scripting
Cross-site scripting
Getting a web app to serve your JavaScript to other users, so it runs in their browser as the site itself.
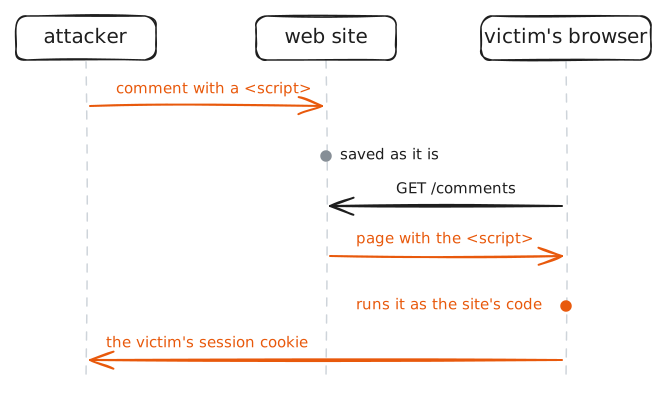
Cross-site scripting (XSS) is getting a web app to serve your JavaScript to other users, so it runs in their browser as the site itself. It happens when input is put into HTML unescaped. Reflected XSS echoes a script from the URL; stored XSS saves it and serves it to every later visitor. The script can read cookies (document.cookie, unless HttpOnly) and send them away. The fix is [[output-encoding]].
Read next
- Output encoding Escaping untrusted data for the exact place it is written, so it is shown as text and never run as code.
- HTTP The web's request and response protocol: plain text over TCP unless wrapped in TLS.
- Content discovery Finding the pages and files a web server holds but links to nowhere, by guessing common paths from a wordlist.
- Cross-site request forgery Making a victim's browser send a state-changing request to a site they are logged in to, from a page the attacker controls.