 Hack the Route Start learning Open app
Web injection and scripting
Parameterised query
Sending a database the fixed query and the values separately, so input is always data and never code.
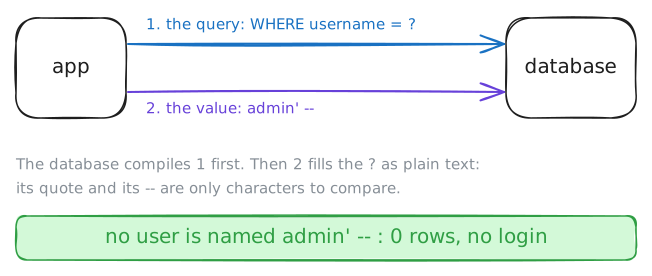
A parameterised (or prepared) query sends the database the SQL with placeholders, WHERE username = ?, and the
values separately, never inside the query text. The database compiles the query first, then binds each value as
data, so a quote or -- in the input is only characters it compares, never SQL it runs. It is the main defence
against [[sql-injection]], alongside least privilege for the web account.