 Hack the Route Start learning Open app
Web injection and scripting
SQL injection
Changing what a database query does by sending input that is pasted into the query as code, not data.
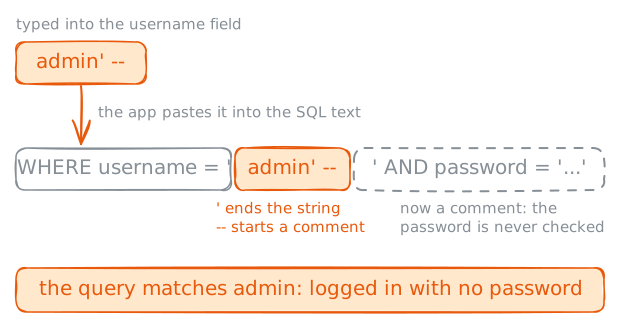
SQL injection is input that changes a query because the app pastes it into the SQL text: ... WHERE username = '<you>'. A quote closes the string and -- comments the rest away, so admin' -- logs in with no password
and ' OR 1=1 -- matches every row. One field can read a whole table. The fix is a [[parameterised-query]]:
fixed SQL, input bound as a value.
Read next
- Parameterised query Sending a database the fixed query and the values separately, so input is always data and never code.
- HTTP The web's request and response protocol: plain text over TCP unless wrapped in TLS.
- Content discovery Finding the pages and files a web server holds but links to nowhere, by guessing common paths from a wordlist.
- Command injection Running your own operating-system commands by sending input a web app pastes into a shell command line.
- Insecure direct object reference Reaching another user's data by changing an id, filename or key in a request the server never checks you own.