 Hack the Route Start learning Open app
Cryptography at work
Salted password storage
Storing a password as a hash of the password plus a per-account random salt, so a precomputed table is useless and two accounts with the same password store different hashes.
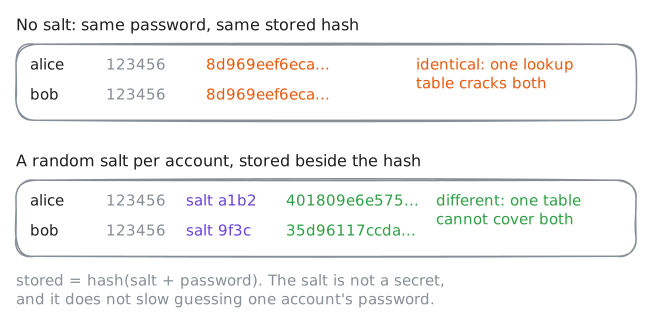
Salted password storage hashes each password with a random salt, one per account, stored in clear beside the [[cryptographic-hash|hash]]. Without it, the same password stores the same digest, so one precomputed table (a rainbow table is a compact one) reads passwords out, and reuse shows. With salts, no single table fits and equal passwords differ. A salt does not slow [[password-cracking|guessing]] one account: pair it with a slow hash ([[hashing-and-salting]]).
Read next
- Cryptographic hash A one-way function that turns any data into a short fixed-size fingerprint, so the same bytes always give the same digest and no one can find two inputs that share one.
- Hashing, salting and key exchange The building blocks under TLS and passwords: one-way hashes, salts, key pairs and agreeing a key in public.
- Password cracking Recovering a password offline by hashing guesses from a wordlist (optionally mangled by rules) until one matches.