 Hack the Route Start learning Open app
Passwords and hashes
Password cracking
Recovering a password offline by hashing guesses from a wordlist (optionally mangled by rules) until one matches.
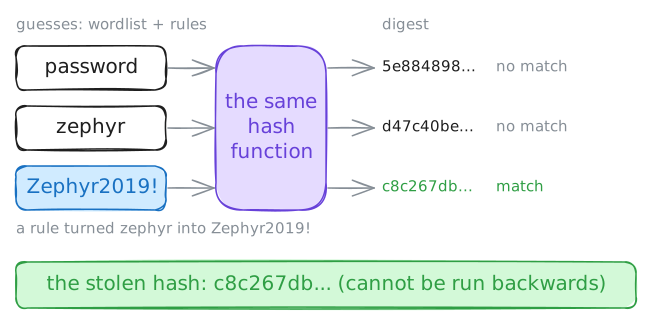
Password cracking recovers a password from its stolen hash by guessing offline. A hash cannot be reversed, so a
cracker (john the ripper, hashcat) hashes each word of a [[wordlist-profiling|wordlist]] the same way and
compares; rules reshape words, zephyr into Zephyr2019!. Hashcat tries only the mode you name (-m 0 is MD5),
so identify the hash first with hashid. The defence: a slow hash and a long random password.
Read next
- Wordlist profiling Building a wordlist from the target's own words and facts, instead of a generic list, so it contains the base word a real passphrase was coined from.
- Hashing, salting and key exchange The building blocks under TLS and passwords: one-way hashes, salts, key pairs and agreeing a key in public.
- Password strength and rate limiting Why guessable passwords fall to repeated tries, and the defences that stop them.
- Key-based authentication Logging in with a private key whose public half the server trusts, instead of a password — so password guessing cannot work.
- Online credential guessing Trying username/password pairs against a live service, as fast as it allows — and why it fails against hardened logins.
- Salted password storage Storing a password as a hash of the password plus a per-account random salt, so a precomputed table is useless and two accounts with the same password store different hashes.