 Hack the Route Start learning Open app
Cryptography at work
weak TLS configuration
A server with a valid certificate that still accepts obsolete protocol versions (TLS 1.0/1.1) or weak cipher suites — a configuration flaw the padlock never shows, found by enumerating what the server offers and fixed by policy, not a new certificate.
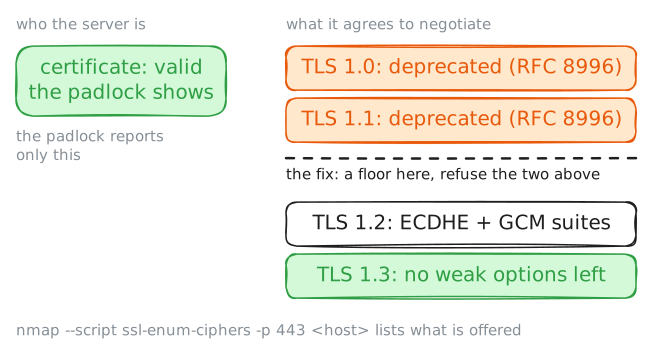
A weak TLS configuration is a server that still accepts old protocol versions or weak cipher suites, even with a valid
certificate. The padlock shows only the certificate. TLS 1.0 and 1.1 were deprecated by RFC 8996; TLS_RSA suites
lack forward secrecy. List the offer with nmap --script ssl-enum-ciphers. The fix is configuration, not a new
certificate: refuse anything below [[tls|TLS]] 1.2, keep ECDHE suites with GCM, enable TLS 1.3.
Read next
- TLS and certificates Encryption plus proof of identity: the server shows a certificate for the name, signed by a trusted authority.
- HTTPS interception Reading an HTTPS session from a box in the path by forging the server's certificate — which works only once the victim trusts the box's CA, and which certificate pinning defeats even then.
- Certificate chain A server's certificate, signed by an issuing CA, whose certificate a root signed: the path a client follows to someone it trusts.
- Self-signed certificate A certificate whose issuer is its own subject: nobody vouches for it but itself.
- Man in the middle A machine placed on the path between two parties, able to read and alter what is not protected end to end.