 Hack the Route Start learning Open app
Web access and file flaws
Broken access control
An access check that rests on something the client controls, so an attacker simply sets it and walks past.
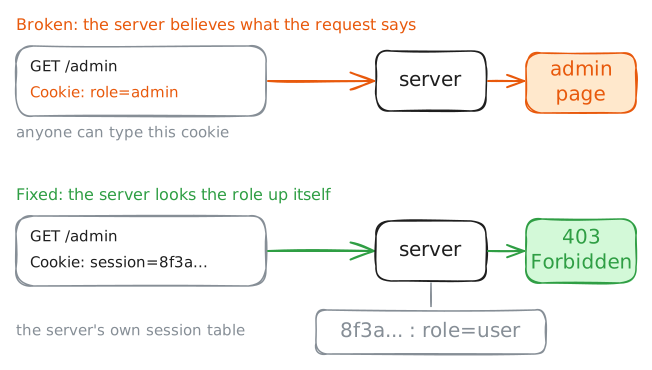
Broken access control is an access check an attacker can walk past, usually because it rests on something the client sends: admitting anyone who sends Cookie: role=admin, hiding only an admin page's link, trusting an isAdmin=true field. Cookies, headers, hidden fields and the URL are all attacker-controlled. [[idor|IDOR]] is the per-object case. The fix: decide on the server from a session it issued, deny by default, check every request.
Read next
- Insecure direct object reference Reaching another user's data by changing an id, filename or key in a request the server never checks you own.
- HTTP The web's request and response protocol: plain text over TCP unless wrapped in TLS.
- Content discovery Finding the pages and files a web server holds but links to nowhere, by guessing common paths from a wordlist.
- Cross-site request forgery Making a victim's browser send a state-changing request to a site they are logged in to, from a page the attacker controls.
- Public cloud storage Cloud object storage is private by default; a single `public` flag makes a bucket answer anyone, credentials or not.
- Least privilege (cloud IAM) A cloud access key should grant only the exact actions and resources its job needs; a wildcard grant hands over far more.