 Hack the Route Start learning Open app
Web access and file flaws
Insecure direct object reference
Reaching another user's data by changing an id, filename or key in a request the server never checks you own.
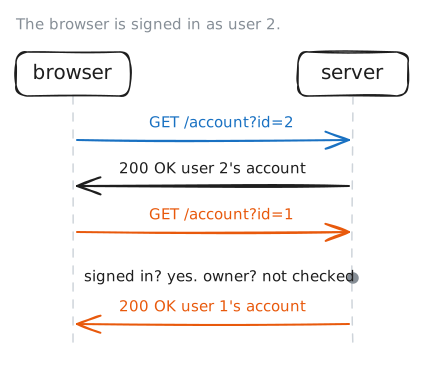
An insecure direct object reference (IDOR) lets a user reach another user's data by changing an id in a request. The request names the object, like /account?id=2, and the server returns it after checking only that you are logged in, so id=1 returns someone else's record. Random ids only make guessing harder. The fix is a server-side check, on every request, that this session may have that object: see [[broken-access-control]].
Read next
- Broken access control An access check that rests on something the client controls, so an attacker simply sets it and walks past.
- HTTP The web's request and response protocol: plain text over TCP unless wrapped in TLS.
- SQL injection Changing what a database query does by sending input that is pasted into the query as code, not data.
- CMS enumeration Reading a known content-management system's exact version, users, themes and plugins, to find its weak spot.
- CMS takeover Chaining a CMS's ordinary conveniences — version disclosure, user enumeration, an unlocked login, admin plugin install — into full control of the site.