 Hack the Route Start learning Open app
Web access and file flaws
CMS enumeration
Reading a known content-management system's exact version, users, themes and plugins, to find its weak spot.
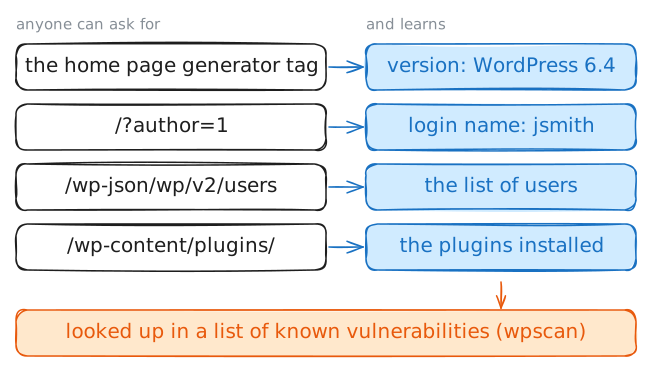
CMS enumeration is reading a content-management system's exact version, users, plugins and themes from what it publishes. On WordPress the version is in the page's generator tag and readme.html; login names leak from ?author=1 and the wp-json API; plugins and themes show under wp-content/. Each is matched against known vulnerabilities, which wpscan automates. The fixes: keep core and plugins updated, remove unused ones, hide user names, turn directory listing off.
Read next
- Content discovery Finding the pages and files a web server holds but links to nowhere, by guessing common paths from a wordlist.
- Insecure direct object reference Reaching another user's data by changing an id, filename or key in a request the server never checks you own.
- HTTP The web's request and response protocol: plain text over TCP unless wrapped in TLS.
- CMS takeover Chaining a CMS's ordinary conveniences — version disclosure, user enumeration, an unlocked login, admin plugin install — into full control of the site.