 Hack the Route Start learning Open app
Web access and file flaws
CMS takeover
Chaining a CMS's ordinary conveniences — version disclosure, user enumeration, an unlocked login, admin plugin install — into full control of the site.
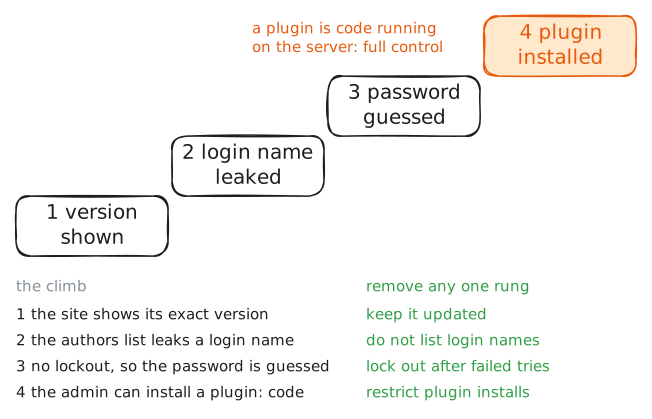
A CMS takeover is gaining full control of a site by chaining small weaknesses of its content-management system. The site shows its version; the authors list leaks the admin's login name ([[cms-enumeration]]); the login has no lockout, so a weak password is guessed; the admin can install a plugin, which runs code on the server. Admin of the CMS is admin of the host. Removing one step breaks the chain.
Read next
- CMS enumeration Reading a known content-management system's exact version, users, themes and plugins, to find its weak spot.
- Online credential guessing Trying username/password pairs against a live service, as fast as it allows — and why it fails against hardened logins.
- Insecure direct object reference Reaching another user's data by changing an id, filename or key in a request the server never checks you own.