 Hack the Route Start learning Open app
Social engineering
Credential harvesting
A page that imitates a real login so the credentials a tricked visitor types are captured by the attacker instead of reaching the real service.
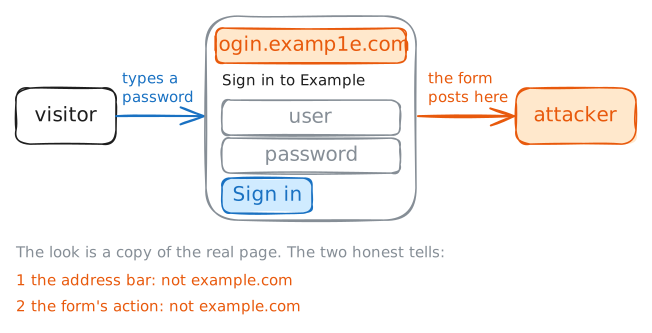
Credential harvesting is capturing logins with a fake sign-in page: a copy of a real login, reached from a
[[phishing]] link, whose form sends what is typed to the attacker. The look is easily copied; the tells are the
origin in the address bar and the form's action. One that relays the login to the real site live defeats a one-time
code; FIDO2/WebAuthn keys, bound to the origin, resist it.
Read next
- Phishing A message that impersonates someone a target trusts to make them act — click a link, hand over a login, open a file — before they think.
- Lookalike domain A domain registered to pass for a real one at a glance — a typo, a swapped letter pair, an extra word or a different ending — used to host phishing, harvesters or misdirected mail.
- Man in the middle A machine placed on the path between two parties, able to read and alter what is not protected end to end.
- Indicators of compromise (IOC) Concrete artifacts of an attack — an address, a file path, a hash — that you block and hunt for everywhere.
- Pretext The believable story a social-engineering attack wraps around its request so the target acts on it without checking.