 Hack the Route Start learning Open app
Social engineering
Lookalike domain
A domain registered to pass for a real one at a glance — a typo, a swapped letter pair, an extra word or a different ending — used to host phishing, harvesters or misdirected mail.
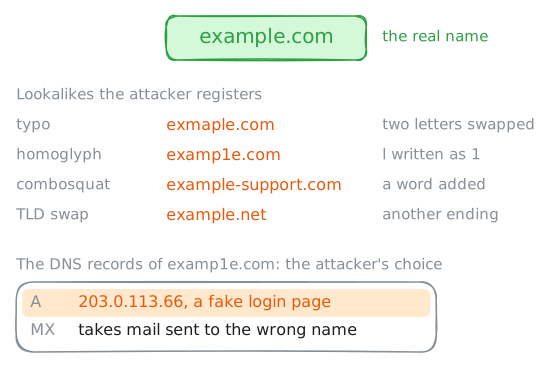
A lookalike domain is a name the attacker really registers, chosen to pass for a real one at a glance.
The kinds: a typo (exmaple.com), a homoglyph (examp1e.com, l as 1), a combosquat that adds a
word (example-support.com) and a TLD swap (example.net). Its [[dns|DNS]] points where the attacker wants: at
a [[credential-harvesting|fake login]], or catching mail. Its own [[email-authentication|SPF, DKIM and DMARC]] pass:
those protect only the exact name.
Read next
- Phishing A message that impersonates someone a target trusts to make them act — click a link, hand over a login, open a file — before they think.
- Credential harvesting A page that imitates a real login so the credentials a tricked visitor types are captured by the attacker instead of reaching the real service.
- DNS The distributed directory that turns names like bank.lab into addresses.
- SPF, DKIM and DMARC Three DNS-published policies that let a receiving mail server check that a message really comes from the domain it claims.