 Hack the Route Start learning Open app
Security foundations
KEV and EPSS
Two public feeds that say whether a flaw is being used: KEV lists flaws seen in real attacks, EPSS forecasts the chance of use in the next 30 days.
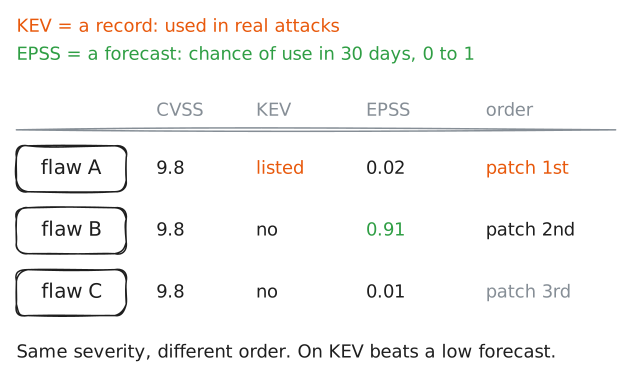
KEV and EPSS are two free public feeds that say whether a flaw with a CVE id is being used. KEV, the Known Exploited Vulnerabilities catalog of the US agency CISA, lists flaws with reliable evidence of use in real attacks: a record. EPSS, kept at FIRST, gives each flaw a daily number from 0 to 1, the estimated chance of use in the next 30 days: a forecast. A KEV entry outranks a low forecast. [[cvss]] rates severity, not use.
Read next
- CVSS and CVE A CVE names a specific known vulnerability; its CVSS score rates how severe it is, so findings can be prioritised.
- Vulnerability management The ongoing loop of scanning a host for weaknesses, prioritising them, fixing them, and rescanning to confirm.
- Vulnerability classes Vulnerabilities sorted by kind, because the kind decides the fix: patch, change, reconfigure, validate, or rotate and remove.
- Security control types Controls sorted by the job each does (prevent, deter, detect, correct, direct, compensate) and by who or what carries each out.