 Hack the Route Start learning Open app
The idea
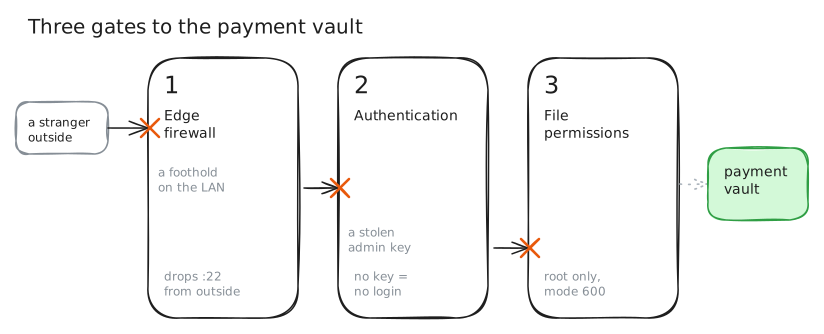
Yara runs the Spoke & Chain bike shop, and its one server holds every customer order and a vault of payment tokens. She is auditing her own defences by walking the path an attacker would take, from a stranger on the public internet to the data itself. Three controls stand in the way; test them one at a time, and see that none of them is the whole wall.
Steps
-
The perimeter: what a stranger can touch
Start where an attacker starts: outside, on
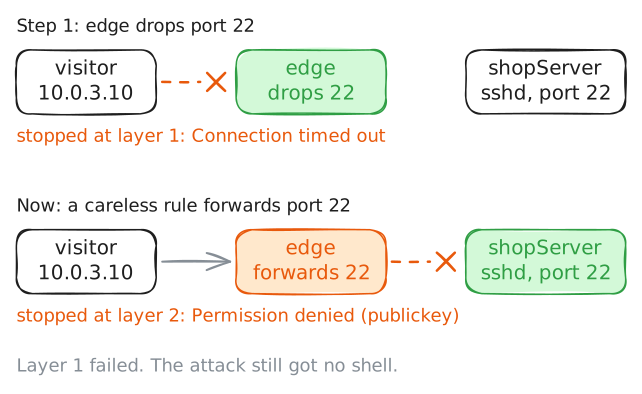
visitor, with no access to anything. Between the public internet and the shop server sits the edge firewall, which forwards the public catalogue on port 80 and drops everything else.So a stranger should be able to read the shop's website, and should not be able to reach the admin shell (SSH, port 22) on the same box. Test both from
visitor.Walking an attacker's path like this is legal here because the shop is Yara's own and the whole lab is sealed off. Outside a lab, probing a system you do not own, and are not authorised in writing to test, is a crime in most countries even when nothing breaks.
visitor:~# curl -sS -m 3 http://10.0.4.10/
visitor:~# ssh -o ConnectTimeout=5 admin@10.0.4.10 hostname
-
The lock on the door: authentication
Suppose the attacker gets past the perimeter: a guest device on the shop Wi-Fi, or the front-desk
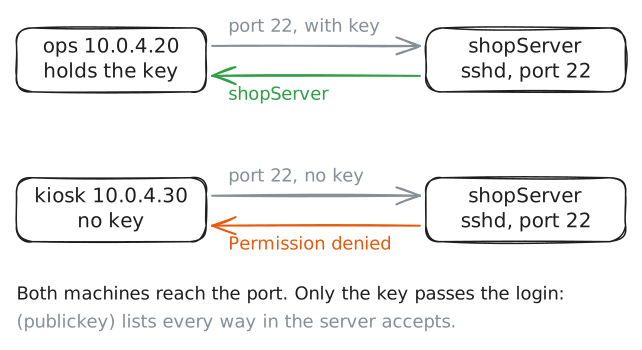
kioskmachine. Now they are on the shop network, where the SSH port answers.Being able to reach a login is not the same as passing it. The shop server's admin login accepts only a key held by Yara's
opslaptop, and password logins are switched off. Log in fromops, then try the same fromkiosk, which has no key.ops:~# ssh admin@10.0.4.10 hostname kiosk:~# ssh -o StrictHostKeyChecking=accept-new admin@10.0.4.10 hostname
-
Least privilege: not every door opens
Now play the worst case: the attacker has Yara's
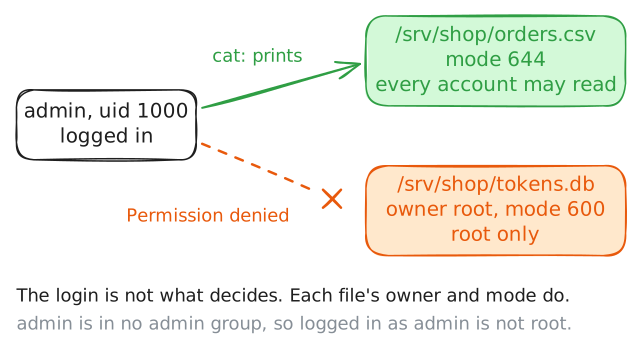
adminlogin. They are on the box, authenticated. Does that hand them the payment vault?On this server the customer orders sit in
/srv/shop/orders.csv, readable by theadminaccount. The payment tokens sit in/srv/shop/tokens.db, owned byrootwith mode 600: the owner may read and write it, and every other account gets nothing. Read both asadmin, then ask the server whoadminreally is.ops:~# ssh admin@10.0.4.10 cat /srv/shop/orders.csv ops:~# ssh admin@10.0.4.10 cat /srv/shop/tokens.db ops:~# ssh admin@10.0.4.10 id
-
Why one layer is never enough
The three controls only earn their keep if beating one does not win the game. Prove it by breaking the outer layer on purpose.
A careless change opens the firewall: a new rule forwards SSH from the outside, exactly the mistake an admin makes under pressure. With the perimeter down, attack the shop server again from
visitor, the stranger with no key, and see whether anything still stops them.edge:~# iptables -I FORWARD 1 -p tcp --dport 22 -j ACCEPT visitor:~# ssh -o StrictHostKeyChecking=accept-new admin@10.0.4.10 hostname
Run these steps on real machines