 Hack the Route Start learning Open app
Detection
Malware signatures (YARA and antivirus)
A pattern that names a known-bad file by its content, so a scanner flags every copy, even renamed or moved.
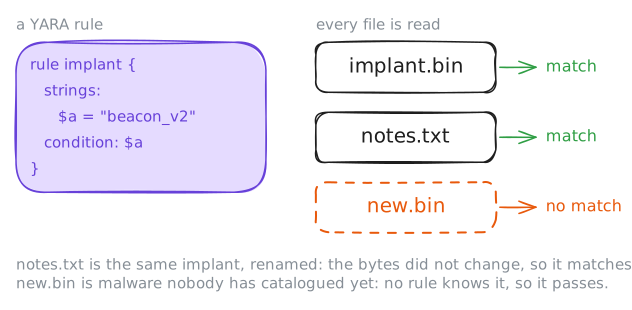
A malware signature is a pattern that identifies a known-bad file by its content. A YARA rule names
strings or byte patterns and a condition over them; an antivirus database (ClamAV's .ndb) holds a pattern
per known sample. A scanner reads every file and reports the matches, so a renamed copy is still caught. It knows only
malware already seen: a new sample passes clean, so [[sandboxing]] sits behind it.
Read next
- IDS signatures and alerts A rule describing a known attack in the traffic's content; the IDS alerts (or, inline, drops) whatever matches.
- Indicators of compromise (IOC) Concrete artifacts of an attack — an address, a file path, a hash — that you block and hunt for everywhere.
- True and false positives An alert's worth is how often it is a real attack versus noise, which decides whether anyone acts on it.
- Sandboxing Running untrusted code or attackers in an isolated environment to observe behaviour without real risk.
- Drive-by download A page that pushes a file to a visitor's machine with little or no consent — the delivery step of an attack, separate from whatever the file then tries to do.