 Hack the Route Start learning Open app
The idea
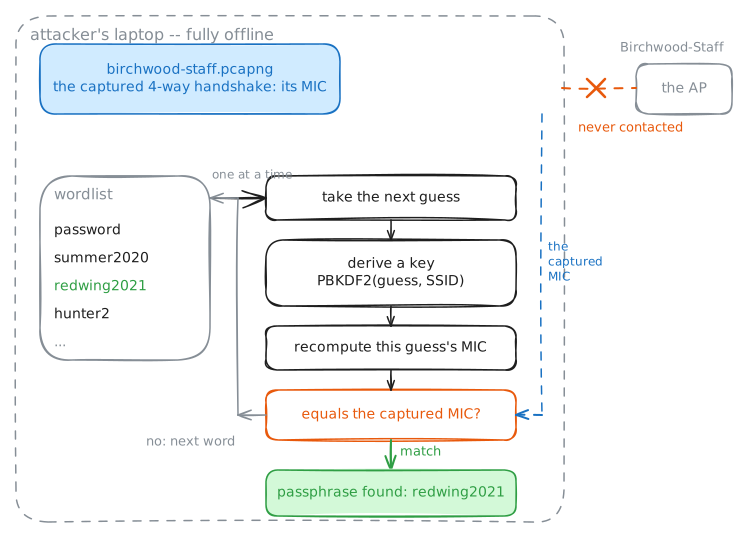
A captured handshake is not the passphrase — it is a hash to test guesses against, offline, as fast as a computer runs. This is the end of the playbook: the handshake you caught on WPA2 network Birchwood-Staff in the last lab, carried here as evidence, turned into the word someone typed into the router. Two tools do the job, and the real skill is knowing which one to reach for — then seeing the one passphrase that beats them both.
Steps
-
Open the handshake you carried in
The last lab ended with a win: the four frames you forced the reception PC to send when you knocked it off Birchwood-Staff. That capture came with you — it is the playbook's evidence, sitting on your box at
/root/birchwood-staff.pcapng.A capture is worth cracking only if the handshake is actually in it, so read it back with
aircrack-ngbefore you spend time on it. Given only a file,aircrack-nglists each network it found and marks one(1 handshake)when the file holds all four of that network's frames; anything less and the crack has nothing to work from, whatever passphrase you try.attacker:~# aircrack-ng /root/birchwood-staff.pcapng
-
Crack it with aircrack-ng
aircrack-ngis the straightforward cracker: point it at the capture and a wordlist, and it works through the list on the CPU, testing each word against the handshake until one matches. It reads the capture directly — no conversion, nothing to set up — which is why it is the tool to reach for when the capture is already in your hand.The attacker's box carries a short list of common passphrases at
/root/wordlist.txt.-w /root/wordlist.txtnames it,-b 02:88:03:0a:10:06picks the network in the capture, and the file comes last. Cracking is exactly this: hash each guess the way the real device did, and stop when the proof matches.attacker:~# aircrack-ng -w /root/wordlist.txt -b 02:88:03:0a:10:06 /root/birchwood-staff.pcapng
-
Crack it with hashcat
hashcatis the speed cracker. It does not read a packet capture, so first convert it withhcxpcapngtool, which writes the handshake as a line in 22000 format — the same format the PMKID route produced in the last lab. Thenhashcat -m 22000runs that hash against the wordlist.-m 22000is the mode number for WPA. In a container with no GPU,--forcelets it run on the CPU; on a real machine a graphics card tests hundreds of thousands of guesses a second, which is why hashcat is the tool for a huge list likerockyou.txtand its fourteen million words.--showafterwards prints what it has cracked.attacker:~# hcxpcapngtool -o /root/clinic.22000 /root/birchwood-staff.pcapng attacker:~# hashcat -m 22000 /root/clinic.22000 /root/wordlist.txt --force attacker:~# hashcat -m 22000 /root/clinic.22000 --show
-
Which one do you reach for?
Both tools recovered the same passphrase, so the choice is about the job, not the result. It is the same split the Passwords road draws between
johnandhashcat: reach for the simple tool when the work is small and in hand, and the fast one when scale and speed decide the outcome.Reach for aircrack-ng when the capture is already in hand, the wordlist is modest, and you want an answer with no setup. Reach for hashcat when the list is huge —
rockyou.txt, a profiled list, rules on top — and the run would take too long any other way. Run hashcat once more below and read theSpeedline it prints: that number, guesses per second, is the whole reason it exists.attacker:~# hashcat -m 22000 /root/clinic.22000 /root/wordlist.txt --force -w 3 --potfile-path /root/fresh.pot
-
The passphrase that beats both
Every crack so far leaned on one thing: the passphrase was a word a list could hold. Change that and the whole attack falls apart, with nothing else touched. The clinic's admin sets a long, random passphrase —
8xQ-vr4T-mn93-Lkd2p— and the reception PC re-joins with it.Capture the new handshake the way you did in the last lab, and run the same wordlist against it. The capture is perfect, the tool is right, the handshake is complete — and the crack still finds nothing, because no wordlist holds a string like that. "Not found" is not a bug here; it is the defender winning.
attacker:~# airmon-ng start wlan0
attacker:~# airodump-ng -c 6 --bssid 02:88:03:0a:10:06 -w /root/clinic-new wlan0mon
attacker:~# aireplay-ng --deauth 10 -a 02:88:03:0a:10:06 wlan0mon
attacker:~# aircrack-ng -w /root/wordlist.txt -b 02:88:03:0a:10:06 /root/clinic-new-01.cap
Run these steps on real machines