 Hack the Route Start learning Open app
Security foundations
Data states
The three places a piece of data can be: kept on a disk (at rest), travelling between machines (in transit), or held by a running program (in use). Each needs its own protection.
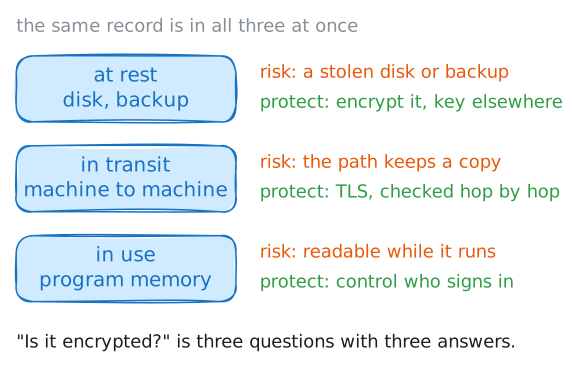
Data states are the three places data can be, each needing its own protection. At rest it sits on a disk or in a backup; encrypting the disk, file or field protects a stolen copy. In transit it travels between machines; [[tls]] protects one hop. In use it sits readable in a running program's memory, where encryption can't cover it; controlling who can sign in to the machine does. "Is it encrypted?" is therefore three questions. See [[tokenisation]] and [[dlp]].
Read next
- Tokenisation Swapping a sensitive value for a random stand-in, the token. The real value stays in one guarded place, the vault, and every other system holds the token.
- CIA triad The three promises a system makes about its data and service: confidentiality, integrity and availability.
- TLS and certificates Encryption plus proof of identity: the server shows a certificate for the name, signed by a trusted authority.
- Hashing, salting and key exchange The building blocks under TLS and passwords: one-way hashes, salts, key pairs and agreeing a key in public.
- Encoding vs encryption Obfuscation hides a payload with reversible transforms — base64, hex, a short XOR — that use no key, so unlike encryption it peels straight back to the original: encoding, not encryption.
- Data loss prevention (DLP) Controls that watch for sensitive data leaving the network and block or flag the attempt.